Archive for category: Blog Posts

What Is Cloud Disaster Recovery? How It Works & Benefits

By the DKBinnovative Crew | Published: July 30, 2026 | Reviewed by Peter Bertran, Chief Client Officer
The short version: Cloud disaster recovery uses cloud infrastructure to back up, replicate, and restore your systems and data after an outage, cyberattack, or disaster — without maintaining a costly second data center. This guide explains how cloud DR works, the RTO and RPO metrics that define it, the main strategies, how it differs from backup and from traditional DR, what a plan should include, the mistakes to avoid, and how to choose the right provider.


Every business runs on data and systems it can’t afford to lose. A ransomware attack, a hardware failure, a flood, or a simple human mistake can take those systems offline in minutes — and for many firms, extended downtime is an existential threat. The question isn’t whether disruption will happen; it’s how fast you can recover. That’s exactly what cloud disaster recovery is built for.

What Is Cloud Disaster Recovery?

Cloud disaster recovery (cloud DR) is a strategy that uses cloud-based infrastructure to back up, replicate, and restore your data and workloads after a disruption — eliminating the need for a costly secondary physical data center. Instead of maintaining duplicate hardware in a second location, you replicate your critical systems to the cloud and spin them back up on demand when something goes wrong.

Because everything runs on cloud infrastructure, recovery can happen in minutes over an internet connection, from almost anywhere. That combination of speed, geographic separation, and pay-as-you-go economics is why cloud-based recovery has largely replaced traditional tape-and-second-site approaches for small and mid-sized businesses.


How Cloud Disaster Recovery Works

Cloud DR follows a straightforward lifecycle:

  • Replication. Your servers, applications, and data are continuously copied to the cloud, so an up-to-date version is always available off-site.
  • Immutable, isolated backups. Copies are stored so they can’t be altered or encrypted by ransomware — a critical safeguard against modern attacks.
  • Failover. When a disaster hits, workloads switch over to the cloud environment, keeping the business running while the primary site is down.
  • Failback. Once the primary environment is restored, systems and data are returned to normal operation.
  • Testing. Recovery is tested regularly so you know — before a real event — that it actually works.

Consider a ransomware scenario. An attacker encrypts your on-premises servers overnight. With cloud DR in place, your team fails over to clean, immutable copies in the cloud, keeps working, and restores the primary environment on your own timeline — instead of negotiating with attackers or losing days of productivity. Platforms such as Microsoft Azure Site Recovery provide the underlying replication and orchestration; the value a partner adds is designing, running, and proving the whole process around your business.

Cloud Backup vs. Cloud Disaster Recovery: What’s the Difference?

These terms are used interchangeably, but they’re not the same thing — and confusing them is one of the most common (and dangerous) mistakes firms make. Cloud backup is a copy of your data stored in the cloud; it answers the question “can I get my files back?” Cloud disaster recovery is a complete capability for restoring your entire operating environment — servers, applications, configurations, and data — and getting the business running again, fast. Backup is a component of DR, not a substitute for it. A firm with backups but no DR plan may eventually recover its data, but could be down for days rebuilding systems from scratch. True cloud DR is about restoring operations, not just files.

RTO vs. RPO: The Metrics That Define Your Recovery

Two metrics sit at the heart of every disaster recovery plan:

  • RTO (Recovery Time Objective) — the maximum acceptable time to get operations back online. If your RTO is one hour, systems must be restored within an hour of an incident.
  • RPO (Recovery Point Objective) — the maximum acceptable amount of data loss, measured in time. A 15-minute RPO means you can afford to lose at most 15 minutes of data.

These two numbers drive every design decision — and your cost. Tighter RTO and RPO targets mean more frequent replication and warmer standby environments. Setting them honestly, based on what downtime and data loss would actually cost your business, is the first real step in any cloud DR plan. Recovery is only half the picture — how a managed IT partner reduces downtime covers the other half.

Cloud DR Strategies: From Backup & Restore to Active-Active

Not every workload needs the same level of protection. The main strategies, from most economical to most resilient:

  • Backup & Restore. Data is backed up to the cloud and restored when needed. Lowest cost, longest recovery time — fine for non-critical systems.
  • Pilot Light. A minimal core of your environment runs in the cloud at all times and scales up during a disaster. Faster recovery at moderate cost.
  • Warm Standby. A scaled-down but fully functional copy of production runs in the cloud, ready to take over quickly.
  • Active-Active. Workloads run simultaneously across multiple locations for near-instant failover. Highest resilience, highest cost.

A good plan mixes these — protecting mission-critical systems with warm standby while backing up lower-priority data more economically. The right blend comes straight from the RTO and RPO you set for each workload.

What a Cloud Disaster Recovery Plan Should Include

A real plan is more than a backup tool. At minimum, it should cover:

  • A prioritized inventory of systems and data, ranked by how critical each is to operations.
  • Defined RTO and RPO targets for each of those systems.
  • Documented roles and responsibilities — who does what when an incident hits.
  • Clear activation triggers — the conditions that declare a disaster and start the plan.
  • A communication plan for staff, clients, and vendors during an outage.
  • A regular testing schedule with documented results.

The plan should be a living document, reviewed as your environment and business change — not a binder that gets written once and forgotten.

Benefits of Cloud Disaster Recovery for SMBs & Professional Firms
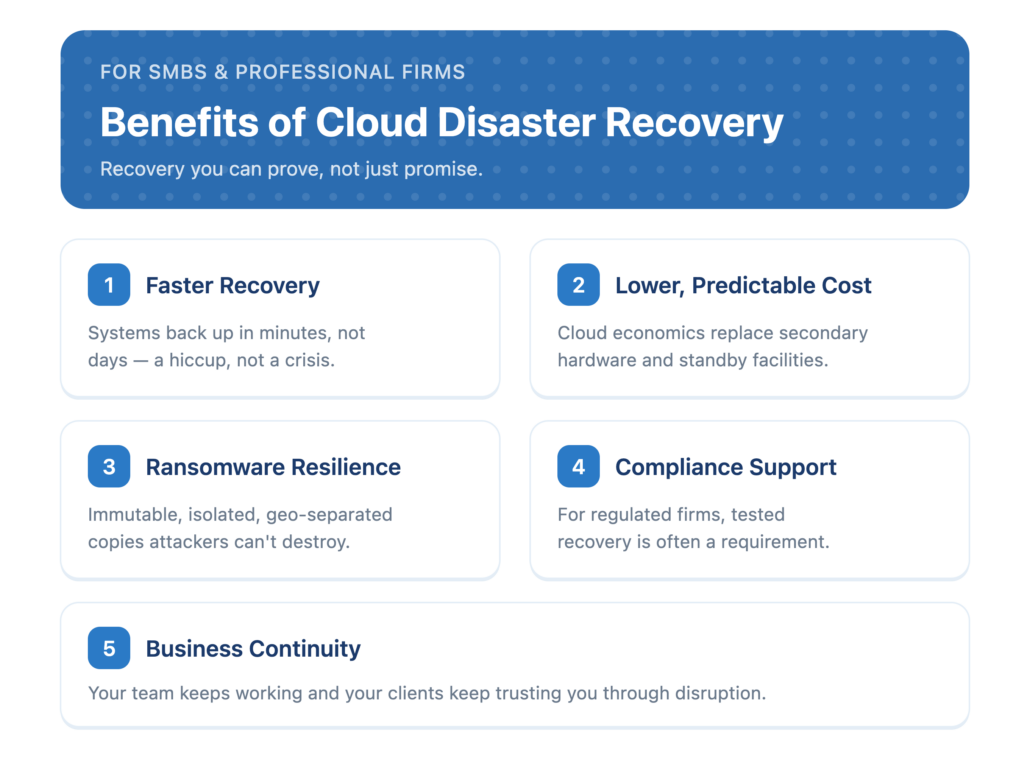
  • Faster recovery. Systems can be spun back up in minutes, not days — the difference between a hiccup and a crisis.
  • Lower, predictable cost. Cloud economics replace expensive secondary hardware and standby facilities.
  • Ransomware resilience. Immutable, isolated, geo-separated copies mean attackers can’t destroy your ability to recover.
  • Compliance support. For regulated firms, tested recovery is often a requirement — see our security & compliance must-haves for how backup fits HIPAA, PCI, and SOC 2.
  • Business continuity. Your team keeps working — and your clients keep trusting you — through events that would sideline an unprepared competitor.

For professional and financial-services firms especially, where client data and uptime are the business, cloud DR isn’t an IT nicety — it’s a fiduciary and regulatory necessity.

Not sure your current backups would actually survive a disaster? Most firms only find out when it’s too late. Explore our managed cloud services to see how we design and prove recovery.

Cloud DR vs. Traditional Disaster Recovery

Traditional disaster recovery meant buying and maintaining a second set of hardware in another data center — expensive, slow to recover, and limited by whatever you owned. Cloud DR removes that burden. Here’s how they compare:

Factor Traditional DR Cloud DR
Infrastructure Duplicate hardware in a second data center Cloud infrastructure, no second site required
Cost model High fixed capital & maintenance Pay-as-you-go, scalable
Recovery speed Hours to days Minutes to hours
Scalability Limited by owned hardware Elastic, on demand

DRaaS: Disaster Recovery as a Service Explained

Disaster Recovery as a Service (DRaaS) takes cloud DR one step further: a provider delivers the entire capability — replication, failover, testing, and support — as a managed service. Instead of building and running cloud DR yourself, you get an expert team that designs the plan, maintains it, and is on the hook to make recovery work when it matters.

For most small and mid-sized firms, DRaaS is the practical choice. Building in-house means licensing tools, configuring replication, and — the part most organizations skip — testing recovery regularly. A managed provider bakes all of that in, so recovery is proven, not assumed. With DRaaS you should expect defined recovery targets, routine tested failovers, and reporting you can hand to auditors and insurers.

Common Cloud Disaster Recovery Mistakes

Most DR plans fail not because of the technology, but because of how they’re managed. The recurring mistakes:

  • Confusing backup with recovery. Having backups is not the same as being able to restore operations quickly.
  • Never testing. An untested plan is a hope, not a plan — the time to discover a gap is not during a real outage.
  • Unrealistic RTO/RPO. Targets set without regard to what the business actually needs, or the budget to meet them.
  • Ignoring ransomware. Backups that aren’t immutable and isolated can be encrypted right alongside production.
  • Set-and-forget. Environments change; a plan that isn’t revisited quietly drifts out of date.

Cloud Disaster Recovery and Compliance

For regulated firms, disaster recovery isn’t optional — it’s expected. Frameworks and rules that touch financial, healthcare, and professional-services businesses (SEC expectations, HIPAA, PCI DSS, and SOC 2) generally require documented, tested processes to protect and restore data. Auditors, examiners, and cyber-insurers increasingly want evidence: a written plan, defined recovery targets, and proof that recovery has actually been tested. A well-run cloud DR program produces exactly that evidence as a byproduct — which is why treating DR as a compliance asset, not just an IT safeguard, pays off. Our guide to security & compliance must-haves covers how this fits the broader picture.

How to Choose a Cloud Disaster Recovery Provider

Not all providers are equal. Evaluate them on:

  1. Defined RTO and RPO commitments — clear targets, not vague promises.
  2. Regular, documented testing — recovery you can prove to auditors, insurers, and leadership.
  3. Ransomware-ready design — immutable, isolated backups as a standard, not an add-on.
  4. Compliance alignment — evidence and reporting that map to your regulatory obligations.
  5. Integration with your IT — DR that works as part of your broader managed IT, not a disconnected point solution.

That last point matters most. When recovery is integrated with the team that runs your day-to-day technology, there’s no finger-pointing during a crisis — one partner owns getting you back online. DKBinnovative designs cloud disaster recovery as part of our managed cloud services, and we support firms across Frisco, Plano, Irving, and the greater DFW metroplex. For the fundamentals, see our glossary entry on backup and disaster recovery.

Business continuity and disaster recovery managed IT services

Business continuity and disaster recovery managed IT services cover two related but separate jobs: keeping the business operating during a disruption, and restoring systems and data afterwards. Disaster recovery answers what you can restore and how fast. Business continuity answers how people keep working while that restore happens, which is the part most plans leave out.

Delivered as a managed service, that means backups monitored and restore-tested on a schedule rather than assumed, documented recovery order so the right systems come back first, alternate access for staff while primary systems are down, and an incident contact list that is current. For regulated firms it also means the evidence of all that, since FINRA Rule 4370 and most cyber insurance renewals ask for a tested plan rather than an intended one.

DKBinnovative delivers this alongside the rest of managed IT for firms in Frisco, Plano and Irving, so the team restoring your systems is the team that already knows them. See our cybersecurity services for how recovery fits with monitoring and incident response.

Frequently Asked Questions

What is disaster recovery in the cloud?

Disaster recovery in the cloud is the process of restoring critical systems and data using cloud-based infrastructure after a disruption such as an outage, cyberattack, or natural disaster. Rather than relying on a second physical data center, your workloads are replicated to the cloud and spun back up on demand, enabling fast recovery and business continuity.

What is the difference between cloud backup and cloud disaster recovery?

Cloud backup is a copy of your data stored in the cloud — it lets you recover files. Cloud disaster recovery is a complete capability for restoring your entire operating environment (servers, applications, configurations, and data) and getting the business running again quickly. Backup is one component of disaster recovery, not a replacement for it.

When would a disaster recovery plan be activated?

A disaster recovery plan is activated when an event genuinely disrupts your IT operations — for example a ransomware attack, major hardware or network failure, data corruption, or a natural disaster that takes systems offline. The plan defines the triggers, roles, and steps so your team can respond immediately instead of improvising during a crisis.

What is one downside of cloud backup?

The main trade-off is dependence on your internet connection and provider: restoring large volumes of data relies on available bandwidth, and you’re trusting a third party with your data. Both are manageable with the right design — appropriate bandwidth planning, encryption, immutable backups, and a reputable, well-integrated provider.

How long does it take to recover after a disaster?

It depends on your Recovery Time Objective (RTO) and the strategy you’ve chosen. A backup-and-restore approach may take hours, while warm standby or active-active designs can restore operations in minutes. The key is setting an RTO that matches what downtime would cost your business and building the plan to meet it.

The Bottom Line

Cloud disaster recovery gives your business a fast, cost-effective, ransomware-resilient way to survive the disruptions that sideline unprepared firms — without the expense of a second data center. The real protection, though, comes from a plan that’s designed for your risk tolerance, integrated with your IT, and tested so you know it works. If you’re not certain your current backups would hold up, now — not during an outage — is the time to find out.

Talk to us about cloud disaster recovery for your firm ?

Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative. For federal guidance on IT contingency planning, see NIST SP 800-34 and Ready.gov Business.
vCIO Services: What a Virtual CIO Does and When to Hire One

By the DKBinnovative Crew | Published: July 30, 2026 | Updated: October 20, 2026 | Reviewed by Peter Bertran, Chief Client Officer

The short version: A vCIO (virtual chief information officer) is a part-time, outsourced technology executive who owns your IT strategy: the multi-year roadmap, the IT budget, vendor decisions, and the quarterly business review that ties technology to business goals. vCIO services give a firm CIO-level planning without a full-time executive hire. At DKBinnovative, a named vCIO is included in every managed IT engagement.


Most business leaders don’t lie awake worrying about servers or software licenses. They worry about growth, risk, budgets, and whether their technology is helping or holding them back. What is a vCIO? It’s the answer to that worry: executive-level IT leadership, on demand.

Below, we explain exactly what a vCIO is, what they do, the benefits, when your firm is ready for one, which businesses gain the most — and how a DKBinnovative vCIO is built to be a genuine strategic partner, not a report generator.

What Is a vCIO (Virtual CIO)?

A virtual CIO, or vCIO, is an outsourced technology executive who provides the same strategic leadership as a full-time CIO, on a flexible basis. Rather than hiring a six-figure executive, your business gets a seasoned IT leader who owns your technology strategy, budgeting, vendor decisions, and long-term roadmap — and translates all of it into plain business terms.

The role sits above day-to-day IT support. A help desk fixes what’s broken; a Chief Information Officer decides where technology should take the business next. A vCIO delivers that higher-altitude thinking as a service — which is why the model has become so popular with small and mid-sized firms that need the strategy without the salary. Crucially, a vCIO isn’t just an outsourced technician with a nicer title; the value is in the judgment, planning, and business alignment they bring to every technology decision.

What Does a vCIO Actually Do?

A vCIO’s job is to make sure your technology is deliberately driving your business forward. Day to day, that looks like:

  • IT strategy & roadmapping — a multi-year plan that maps technology to your business objectives, not a pile of disconnected tools.
  • Technology budgeting — forecasting spend, planning hardware and software lifecycles, and removing surprise costs.
  • Risk & security oversight — making sure cybersecurity, compliance, and business continuity are actually addressed at a leadership level.
  • Vendor management — evaluating and coordinating the providers and platforms your business relies on.
  • Business alignment — translating technology into outcomes leadership cares about: efficiency, growth, and reduced risk.

Much of this happens on a predictable cadence — typically a quarterly business review where your vCIO reports on progress, revisits the roadmap, flags emerging risks, and adjusts the plan as your business changes. Done well, a vCIO turns IT from a reactive cost center into a planned, measurable driver of the business.

What Do vCIO Services Include?

vCIO services cover the strategic side of IT that a help desk never touches. A typical engagement includes:

  • Technology roadmap covering the next one to three years of hardware, software, and cloud decisions
  • IT budget planning so refreshes and licensing are forecast, not surprises
  • Quarterly business reviews that report on uptime, security, and projects against your goals
  • Vendor management for line-of-business software, carriers, and cloud providers
  • Security and compliance alignment with your vCISO and your regulators
  • Secure AI planning, including how staff can use AI tools such as Hatz.AI without exposing client data

DKBinnovative vCIO discussing technology strategy with a professional services firm

How a Virtual CIO Builds Your Technology Roadmap

The technology roadmap is the vCIO’s central deliverable — the document that turns “we should probably upgrade that someday” into a deliberate plan. It usually starts with an assessment of your current environment: what you have, what’s aging out, where the security and compliance gaps are, and where technology is slowing the business down. From there, the vCIO maps initiatives to your business goals over a one-to-three-year horizon, sequences them by priority and budget, and ties each to a measurable outcome. The result is a plan leadership can actually understand and approve — no jargon, no surprises — and a clear answer to the question every executive eventually asks: “where is our technology headed, and why?”

Do You Need a vCIO? Signs Your Firm Is Ready

You don’t need to be an enterprise to benefit from a virtual CIO. These are the common signals that it’s time:

  • Technology decisions are made reactively, one emergency at a time.
  • Your IT spend feels unpredictable and hard to justify.
  • You’re facing compliance pressure (SEC, HIPAA, PCI, cyber-insurance) and need a documented strategy.
  • Leadership can’t get a clear, non-technical answer to “where is our technology headed?”
  • You’re growing, merging, or opening locations and technology needs to scale with you.

What to Look For in a vCIO Provider

Five things separate a real vCIO from an account manager with a new title:

  1. A named person. You should know who your vCIO is, and it should be the same person every quarter.
  2. A written roadmap. Ask to see a sample. If the provider cannot show one, the role is reactive.
  3. Industry experience. An RIA, a CPA firm, and a law firm each face different regulators. Your vCIO should know yours.
  4. Quarterly reviews with data. Uptime, ticket trends, security posture, and project status, not a slide of logos.
  5. Independence from the sale. Recommendations should follow your plan, not a quota.

Which Businesses Benefit Most From a Virtual CIO?

Almost any organization can use strategic technology leadership, but a few types gain the most from a virtual CIO. Regulated and professional-services firms — registered investment advisers, wealth managers, accounting and CPA firms, and law practices — face serious compliance and cybersecurity obligations without the scale to justify a full-time CIO, so a vCIO fills a real gap. Growing small and mid-sized businesses benefit when technology decisions start outpacing the leadership team’s bandwidth. And firms going through change — a merger, an acquisition, a new office, or rapid hiring — need someone to make sure technology scales with the business instead of becoming the bottleneck. If your technology carries real risk or is central to how you serve clients, a vCIO earns its place quickly.

Wondering whether a vCIO is right for your business? Our team can walk you through what strategic IT leadership would look like for your firm. Explore our IT consulting services.

7 Benefits of Hiring a vCIO

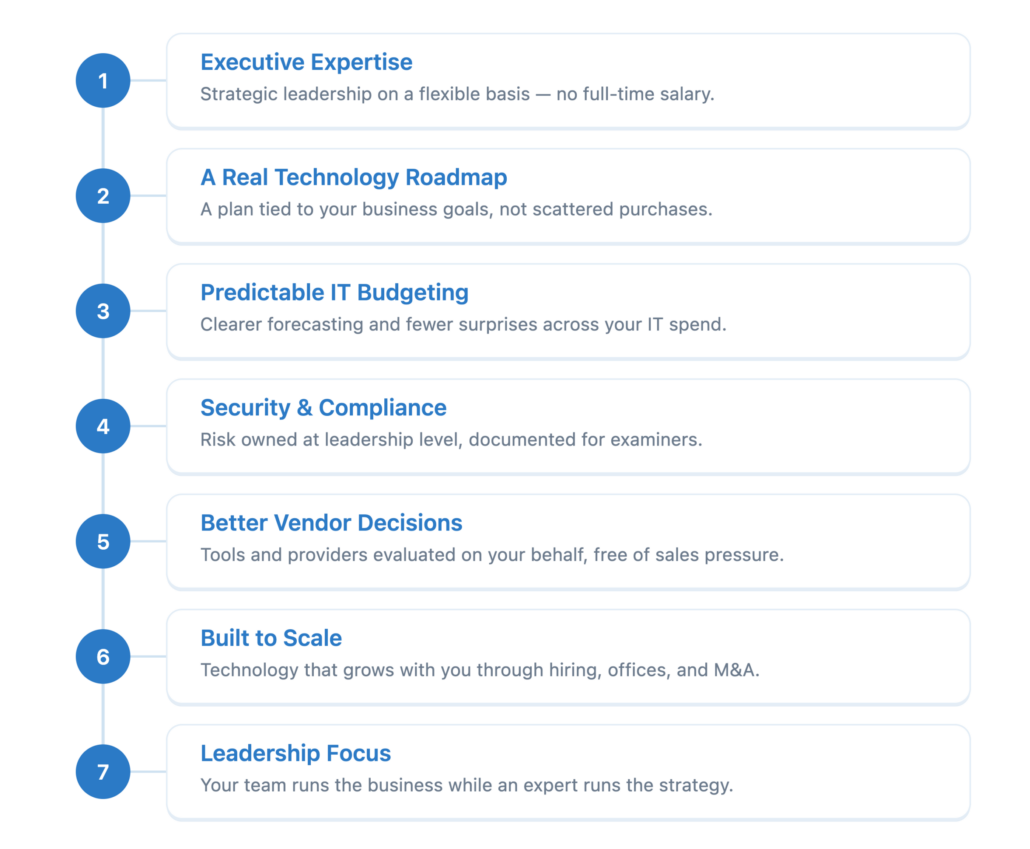
  1. Executive expertise without the executive salary. Strategic leadership on a flexible, scalable basis, so you pay for the guidance you need rather than a full-time headcount.
  2. A real technology roadmap. A plan tied to your goals instead of scattered, reactive purchases — so every dollar has a purpose.
  3. Predictable IT budgeting. Fewer surprises, clearer forecasting, and smarter spend across hardware, software, and services.
  4. Stronger security and compliance. Risk managed at the leadership level, with the documentation examiners and insurers expect.
  5. Better vendor decisions. An expert evaluating tools and providers on your behalf, free of sales pressure.
  6. Scalability. Technology that grows with you through hiring, new offices, or mergers and acquisitions.
  7. Focus. Your leadership team stays on the business while an expert owns the technology strategy.

vCIO vs. In-House CIO vs. Managed IT

These roles are easy to confuse. Here’s how they differ:

Role What it is Best for
vCIO Outsourced IT executive setting strategy, budget & roadmap SMBs and professional firms that need strategy, not a full-time hire
In-house CIO Full-time C-level employee owning technology Larger organizations with the scale to justify the salary
Managed IT Ongoing support, monitoring & maintenance of your environment Any business needing reliable day-to-day operations

The strongest setup pairs them: a vCIO sets the direction while managed IT services — or co-managed IT alongside your internal team — execute it. Strategy and delivery working as one system.

Virtual CIO vs. Fractional CIO

The terms overlap, and providers use them loosely. In practice:

Virtual CIO (vCIO) Fractional CIO
Typical engagement Part of an ongoing managed IT relationship Standalone executive retainer
Time commitment Quarterly reviews plus on-demand planning A set number of days per month
Best fit Small and mid-sized firms that want strategy tied to day-to-day IT Larger firms with an internal IT team that needs executive leadership

vCIO vs. vCISO: Strategy Meets Security

As firms take security more seriously, another role enters the picture: the vCISO (virtual Chief Information Security Officer). The simplest way to keep them straight is by focus. A vCIO owns overall technology strategy — roadmap, budget, vendors, and business alignment. A vCISO owns information security specifically — the security program, risk posture, and compliance controls. In smaller organizations one advisor may wear both hats; in more regulated or higher-risk firms, the two work as partners, with security getting its own dedicated leadership. For firms that need that deeper security focus, we also offer vCISO services for family offices and investment firms.

vCIO Services for Investment and Professional Firms

DKBinnovative team supporting a DFW professional services firm

For RIAs, CPA firms, and law firms, the vCIO’s roadmap has to answer to a regulator as well as a budget. DKBinnovative vCIOs plan around SEC Regulation S-P for investment advisers, IRS Publication 4557 and the FTC Safeguards Rule for accounting firms, and ABA confidentiality duties for law firms. That means the roadmap includes the documentation an examiner or auditor will ask for, not just the next hardware refresh.

See managed IT for RIAs, accounting firms, and law firms.

How vCIO Services Are Priced

At DKBinnovative, vCIO leadership is included in every managed IT engagement rather than sold as a separate retainer. The engagement is a fixed monthly fee, quoted after a complimentary discovery call, so strategy is never the line item that gets cut when budgets tighten.

vCIO Services in Frisco, Plano, and Irving

DKBinnovative’s vCIOs work from our Frisco headquarters and our Plano and Irving offices, and meet clients on site when needed. For firms across Collin and Dallas counties, that means your strategic lead also knows your office, your network, and your team. Learn more about managed IT in Frisco, Plano, and Irving.

The DKBinnovative Difference: A Strategic Partner, Not a Report Generator

Plenty of providers will hand you a vCIO who runs a quarterly report and disappears. At DKBinnovative, we do vCIO differently. Your vCIO acts as your strategic advisor and partner — someone who takes the time to understand your business goals and then aligns your technology to reach them.

That means your DKBinnovative vCIO is in the room on the decisions that matter: where to invest, what risks to close, how to keep you compliant, and how technology can accelerate the outcomes your leadership cares about. It’s the difference between “here’s a status update” and “here’s how we move your business forward.” We start by learning your business — your goals, your clients, your pressures — and only then do we shape the technology plan around them, revisiting it as your priorities shift.

Good technology leadership is ultimately about aligning technology with business direction — a principle even national cyber authorities stress in their board-level guidance. That alignment is exactly what a DKBinnovative vCIO is built to deliver.

How to Get Started With a vCIO

Bringing on a vCIO is simpler than most leaders expect. It usually starts with a conversation about your business goals and current technology, followed by an assessment of where the gaps and risks are. From there, your vCIO builds the roadmap, sets the budget, and starts guiding decisions — as an ongoing partner, not a one-time project. There’s no need to rip out what’s working; a good vCIO meets your environment where it is and improves it deliberately over time.

Frequently Asked Questions

What is the difference between a vCIO and a CIO?

A CIO is a full-time, in-house technology executive. A vCIO (virtual CIO) delivers the same strategic leadership — IT roadmap, budgeting, risk oversight, and vendor management — as an outsourced service on a flexible basis, so smaller firms get executive-level guidance without a full-time salary.

What does a vCIO do?

A vCIO owns your technology strategy: building a multi-year IT roadmap aligned to your business goals, planning and forecasting your IT budget, overseeing cybersecurity and compliance at a leadership level, managing vendors, and translating technology into business outcomes for your leadership team.

How is a vCIO different from managed IT?

Managed IT keeps your technology running day to day — support, monitoring, patching, and maintenance. A vCIO works a level up, owning the strategy behind it: what to invest in, what to retire, how to budget, and how technology should support your goals. The two are complementary, and they work best together — strategy setting the direction, managed IT executing it.

Is a CIO higher than a CISO?

They are different roles. A CIO (or vCIO) owns overall technology strategy and operations, while a CISO (or vCISO) focuses specifically on information security and risk. In many organizations security reports up through the CIO, but the two are partners — strategy and security — rather than a strict hierarchy.

Do small businesses need a vCIO?

Many do. Small and mid-sized firms often face the same technology risks and compliance demands as large ones, but without an in-house executive to plan for them. A vCIO gives them that strategic leadership on a scale and budget that fits — which is why the model is popular with professional and financial-services firms.

What does vCIO stand for, and what are its responsibilities?

vCIO stands for virtual chief information officer. A vCIO is responsible for IT strategy, the technology roadmap, IT budgeting, vendor management, and quarterly business reviews, delivered part-time by an outsourced provider instead of a full-time executive.

Can a virtual CIO work with our existing MSP or IT team?

Yes. A vCIO can lead strategy while an internal team or another provider handles daily support. At DKBinnovative, the vCIO is part of the managed or co-managed engagement, so planning and execution stay connected.

What is the difference between a vCIO and a fractional CIO?

A vCIO usually comes as part of an ongoing managed IT relationship with quarterly reviews. A fractional CIO is typically a standalone executive retainer for a set number of days each month, more common at larger firms with their own IT staff.

The Bottom Line

A vCIO gives your business the executive-level technology leadership it needs to grow, stay secure, and spend smart — without hiring a full-time CIO. The real value, though, comes from having a vCIO who acts as a true partner. That’s the standard we hold at DKBinnovative: technology aligned to your goals, guided by an advisor who’s genuinely in it with you.

Talk to us about vCIO and IT consulting for your firm ?

Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative.


SEC “AI Washing” Enforcement in 2026: What DFW Investment Advisers Must Know

Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative

Artificial intelligence has moved from pilot projects to the front lines of how investment advisers market themselves and run their operations. But as AI claims have multiplied, so has regulatory scrutiny. The U.S. Securities and Exchange Commission has made “AI washing” — overstating or misrepresenting how a firm uses AI — an enforcement priority, and DFW registered investment advisers (RIAs) are not exempt. This guide explains what AI washing is, the enforcement precedents that set the tone for 2026, how to tell whether your firm is exposed, and what documentation keeps you exam-ready.

What is “AI washing,” and why is the SEC targeting it?

AI washing is the practice of exaggerating, misstating, or failing to substantiate the role of artificial intelligence in a firm’s products, services, or investment process. It borrows its name from “greenwashing,” where companies overstate environmental credentials. For investment advisers, AI washing usually shows up in marketing: claiming an “AI-driven” strategy that is largely manual, implying proprietary models the firm actually licenses from a vendor, or promising predictive capabilities the technology cannot deliver.

The SEC treats these as disclosure and marketing violations. Under the Marketing Rule (Rule 206(4)-1) and the antifraud provisions of the Investment Advisers Act, every public statement an adviser makes must be fair, balanced, and substantiated. An AI claim you cannot prove is, in the SEC’s view, a misleading claim.

What SEC AI-washing enforcement actions set the precedent?

The enforcement pattern began in March 2024, when the SEC charged two investment advisers — Delphia (USA) Inc. and Global Predictions Inc. — for making false and misleading statements about their use of AI. Both firms settled and paid civil penalties. In announcing the actions, SEC leadership warned the industry plainly: if you claim to use AI, you must be able to back it up, and you cannot promise capabilities you do not have.

That precedent has only hardened. AI adoption across advisory firms has accelerated, examiners now routinely ask about AI use during exams, and marketing claims that were once aspirational are measured against what the technology actually does. For 2026, the takeaway is simple: the bar for substantiating AI claims is higher than ever, and “everyone says it” is not a defense.

Is your firm at risk? Five signs of AI-washing exposure

  • Marketing outpaces reality. Your website or pitch deck describes “AI-powered” investing, but the day-to-day process is largely manual or rules-based.
  • Vendor AI presented as proprietary. You license an AI tool from a third party but imply the model is your own.
  • No documentation behind the claim. You cannot produce a written record of what the AI does, who oversees it, and how outputs are validated.
  • Unbounded predictive language. Marketing promises the AI will “predict” markets or “guarantee” outcomes.
  • Shadow AI in operations. Employees paste client data into consumer AI tools outside any governed, documented framework.

What documentation proves your AI claims to SEC examiners?

Substantiation is the heart of AI-washing defense. Examiners want to see that every public claim maps to a documented reality. Build and maintain:

  • An AI model inventory — every AI system in use, whether built or licensed, what it does, and what data it touches.
  • Vendor attestations — written confirmation from AI vendors describing the technology, its limits, and how customer data is handled.
  • Marketing substantiation files — for each public AI claim, the evidence that supports it, reviewed before publication.
  • Human-oversight records — proof that qualified people review and validate AI outputs, especially anything touching investment decisions.
  • Data-handling and security controls — how client data is protected when it flows through AI systems, aligned with SEC Regulation S-P.

How should RIAs govern AI across marketing and operations?

The firms least exposed to AI washing treat AI as a governed program, not an ad-hoc tool. That means a written AI governance policy that defines approved tools, prohibited uses, data-handling rules, review workflows for AI-related marketing, and an accountable owner. It also means closing the gap between marketing and compliance so no AI claim reaches the public without substantiation — and controlling “shadow AI,” where staff quietly route client information through ungoverned consumer tools.

Governance and security are two sides of the same coin. A documented, secure AI environment is exactly what lets you make confident, provable AI claims — and exactly what an examiner wants to see.

How DKBinnovative helps investment firms deploy secure, documented AI

DKBinnovative has supported DFW investment and professional-services firms since 2004, and secure, compliant AI is now a core part of that work. We help RIAs stand up governed AI through Hatz.AI — a secure, private AI platform built for regulated firms — so your team gets the productivity of AI inside an environment you can document and defend. Combined with our virtual CISO (vCISO) service, we deliver the model inventory, vendor oversight, human-in-the-loop controls, and Reg S-P-aligned security that turn AI from an examination risk into a substantiated advantage. Explore our approach to secure AI for investment firms and managed IT for RIAs.

Concerned your AI claims could draw SEC scrutiny? Talk with DKBinnovative about a secure, documented AI program, or call (888) 352-4832 to reach a local advisor.

Frequently Asked Questions

What is AI washing?

AI washing is overstating, misstating, or failing to substantiate how a firm uses artificial intelligence in its products, services, or investment process. For investment advisers, the SEC treats unsupported AI claims as marketing and disclosure violations under the Marketing Rule and the Investment Advisers Act’s antifraud provisions.

Can the SEC fine an RIA for exaggerating its AI use?

Yes. In March 2024 the SEC charged two advisers for false and misleading AI statements, and both settled with civil penalties. Any public AI claim an adviser cannot substantiate can expose the firm to enforcement, penalties, and remediation requirements.

How do we prove our AI claims to SEC examiners?

Maintain an AI model inventory, vendor attestations, marketing substantiation files, and human-oversight records — documentation that maps every public AI claim to what the technology actually does and who validates it.

Does using a third-party AI tool count as “our AI”?

You can use licensed AI, but you must describe it accurately. Implying that a vendor’s model is proprietary, or overstating what it does, is a common form of AI washing. Disclose the role of third-party tools truthfully and keep vendor attestations on file.

How does AI governance connect to Reg S-P?

SEC Regulation S-P requires advisers to protect customer information and maintain a written incident-response program. Because AI systems often process client data, your AI governance and your Reg S-P safeguards must work together — controlling how data flows through AI tools is both a security and a compliance requirement.


The Small Business Cybersecurity Checklist (2026)

By DKBinnovative Team | Published: June 22, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: A cybersecurity checklist gives a DFW small or midsize business a clear, repeatable set of controls to put in place and verify. The essentials: enforce multi-factor authentication everywhere, deploy endpoint detection and response (EDR) with 24/7 monitoring, secure email and verify every wire out-of-band, keep immutable restore-tested backups, segment your network, train your people, document a written security plan, and have an incident-response plan ready. DKBinnovative has implemented this checklist for DFW businesses and professional firms since 2004.

Key takeaways:

  • A cybersecurity checklist turns vague “be more secure” goals into concrete, verifiable controls.
  • Most DFW breaches are stopped by a short list of well-implemented fundamentals.
  • MFA, EDR, immutable backups, and out-of-band wire verification carry the most weight.
  • Investment and professional firms must map the checklist to their compliance obligations.
  • The checklist is only effective when it is enforced and reviewed — not filed away once.

If your DFW business needs a cybersecurity checklist to protect against evolving threats, you are in the right place. The frequency of cyberattacks is rising, and small and midsize businesses (SMBs) across Dallas–Fort Worth need reliable, repeatable protection. At DKBinnovative, we help DFW businesses safeguard their operations with the comprehensive cybersecurity checklist below — the same security baseline we enforce for investment and professional firms. For the wider context on the threats driving this, see our pillar guide on securing your DFW business against rising cybersecurity threats.

Cybersecurity checklist for DFW small and midsize businesses from DKBinnovative

What is a cybersecurity checklist, and why do DFW SMBs need one?

A cybersecurity checklist is a structured list of the security controls a business should implement, verify, and maintain. It converts a broad goal — “protect the company” — into specific, checkable actions, so nothing critical is left to chance. For a DFW small or midsize business without a full-time security team, that structure is the difference between assuming you are protected and knowing you are.

DFW’s fast-growing, data-rich economy makes its SMBs attractive targets, and attackers increasingly automate their campaigns with AI. A checklist keeps your defenses current, gives leadership a clear view of where the gaps are, and produces the evidence that cyber-insurance carriers, clients, and — for regulated firms — examiners now expect.

The top cybersecurity threats facing DFW SMBs

A handful of attack types cause the majority of real-world losses for DFW businesses. Your checklist exists to close exactly these gaps:

  • Business email compromise (BEC) and wire fraud — attackers impersonate a principal, client, or vendor to redirect a payment. The single costliest threat for firms that move money; DFW law and CPA firms are especially targeted.
  • Ransomware — malware that encrypts your data and halts operations until you pay or restore.
  • AI-driven phishing — polished, error-free lures and voice deepfakes that defeat old “spot the typo” advice.
  • Account takeover — stolen or reused credentials used to log in as a trusted employee.
  • Vendor and third-party compromise — an attack that reaches you through a trusted partner or software provider.

The essential cybersecurity checklist for DFW businesses

Work through these eight categories in order — most breaches are stopped before they start by getting the fundamentals right and keeping them enforced.

1. Identity and access

  • Enforce multi-factor authentication (MFA) on every account, especially email and remote access.
  • Apply least-privilege access — staff get only what their role requires.
  • Use a company password manager and ban reused or shared passwords.
  • Disable accounts the same day an employee leaves.

2. Devices and endpoints

  • Deploy endpoint detection and response (EDR) on every workstation and server.
  • Patch operating systems and software on a defined schedule.
  • Encrypt laptops and mobile devices, and manage them with a device-management platform.

3. Email and phishing defense

  • Turn on advanced email security and configure SPF, DKIM, and DMARC.
  • Verify every wire transfer and banking-detail change out-of-band — a callback to a known number.
  • Run continuous security-awareness training with simulated phishing.

4. Data and backups

  • Keep immutable backups that ransomware cannot encrypt, following a 3-2-1 strategy.
  • Test restores regularly and define a recovery-time objective.

5. Network and cloud

  • Run a managed firewall, segment your network, and secure remote access.
  • Lock down Microsoft 365 and Azure with conditional access and identity protection.

6. People, policy, and AI

  • Maintain a written information security plan and acceptable-use policy.
  • Adopt an AI usage policy and a secure, firm-controlled AI platform such as Hatz.AI so staff can use AI without leaking confidential data to public models.

7. Monitoring and incident response

  • Monitor 24/7 with a Security Operations Center and centralized logging.
  • Document and rehearse an incident-response plan, and keep cyber insurance current — our cyber insurance renewal checklist shows what carriers now require.

8. Compliance mapping

Regulated firms should map the controls above to their obligations: the FTC Safeguards Rule, SEC Regulation S-P for advisers, IRS Publication 4557 for tax practices, and SOC 2. The federal CISA small-business guidance is a useful cross-reference. New to the terminology? Our IT, cybersecurity, and compliance glossary explains each term in plain language.

How DKBinnovative can help

DKBinnovative has secured Dallas–Fort Worth businesses — with a particular focus on investment and professional firms — since 2004, more than 22 years. We implement and maintain every item on this checklist as standard scope: MFA and EDR enforced by default, an in-house 24/7 help desk and Security Operations Center, immutable backups, named virtual CISO leadership, and compliance documentation mapped to the frameworks your firm answers to. Already have internal IT? Our co-managed IT services add the security muscle and coverage your team needs without new hires. Our help desk measured a 3-minute average first response, a 78% first-call resolution rate, and 98.14% client satisfaction in 2025.

Request your free cybersecurity assessment or call (888) 352-4832 and we will benchmark your business against this checklist and close the gaps.

Frequently Asked Questions

What is a cybersecurity checklist?

A cybersecurity checklist is a structured list of the security controls a business should implement, verify, and maintain — covering identity and access, devices, email, backups, network, people, monitoring, and compliance. It turns a broad goal into specific, checkable actions so nothing critical is overlooked.

What should be on a DFW small business’s cybersecurity checklist?

At minimum: multi-factor authentication everywhere, endpoint detection and response with 24/7 monitoring, advanced email security with out-of-band wire verification, immutable restore-tested backups, network segmentation, continuous security-awareness training, a written information security plan, and a documented incident-response plan. Regulated firms add compliance mapping.

What is the most important item on the checklist?

There is no single control, but multi-factor authentication and out-of-band wire verification prevent two of the most common and costly attacks — account takeover and business email compromise — while immutable backups make ransomware survivable. Implemented together, these carry the most weight for most DFW SMBs.

How often should a DFW business review its cybersecurity checklist?

Review the checklist at least quarterly, and again after any major change — new staff, a new application, an office move, or an incident. Cyber-insurance renewals and compliance exams are also natural review points. A checklist only protects you when it is kept current and enforced.

Do DFW investment and professional firms need a different checklist?

The core controls are the same, but investment advisers, accounting firms, and law firms must map them to obligations such as SEC Regulation S-P, the FTC Safeguards Rule, IRS Publication 4557, and SOC 2, and produce audit-ready documentation. DKBinnovative builds that mapping into the engagement.

Can DKBinnovative implement the checklist for us?

Yes. DKBinnovative implements and maintains every item on this checklist for DFW businesses — fully managed or co-managed alongside your internal team — and provides the documentation regulators, clients, and insurers expect. Call (888) 352-4832 or request a free assessment to get started.

Secure Your Financial Firm: Premium IT Support Solutions in Frisco!

By DKBinnovative Team | Published: June 16, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: A small financial firm in Frisco needs IT support built for its regulatory profile, not generic help desk service. That means a provider fluent in SEC Regulation S-P, FINRA rules, the FTC Safeguards Rule, and SOC 2 — with an enforced security baseline (MFA and EDR), immutable backups, an in-house 24/7 help desk and Security Operations Center, virtual CISO leadership, and same-day on-site support across Frisco. DKBinnovative has delivered exactly this for Frisco financial, RIA, and wealth-management firms since 2004.

Key takeaways:

  • Financial firms are held to security standards generic IT providers rarely document.
  • SEC Regulation S-P, FINRA, and the FTC Safeguards Rule make security a compliance obligation, not an option.
  • The biggest financial threat is wire fraud via business email compromise (BEC).
  • Premium IT support means security and compliance are standard scope, not upsells.
  • Local, same-day Frisco support matters when a remote fix is not enough.

Frisco has become one of the fastest-growing business hubs in Texas — corporate headquarters at The Star, Frisco Station, and Hall Park, and a rising concentration of investment advisers, wealth managers, accounting practices, and other financial firms along the Dallas North Tollway. For those firms, IT is not just productivity; it is part of their security posture and their compliance record. This guide explains what premium IT support in Frisco looks like for a small financial firm, and how to choose a provider that protects both your clients and your examination history.

What makes IT support different for a financial firm?

A financial firm’s IT provider is part of its regulatory and security posture — so the bar is far higher than for a typical small business. A generic Frisco IT company can keep email running; a financial-services specialist also produces the documented controls an examiner, auditor, or cyber-insurance carrier will accept. The difference shows up the moment a regulator asks for evidence or an attacker targets a wire.

For a small investment adviser, wealth manager, or accounting firm, the right partner treats security and compliance as standard scope — not as premium tiers added on after a breach or a deficiency letter.

What compliance frameworks must Frisco financial firms meet?

Financial firms in Frisco operate under overlapping cybersecurity mandates that a specialist IT partner builds into the engagement.

  • SEC Regulation S-P — safeguards and incident-response requirements for registered investment advisers.
  • FINRA rules — recordkeeping and supervision expectations for broker-dealers.
  • FTC Safeguards Rule and Gramm-Leach-Bliley — a written information security program for firms handling financial data.
  • SOC 2 — the controls clients and partners increasingly require proof of.
  • Texas SB 2610 — a state cybersecurity safe harbor for firms that adopt a recognized framework.

A provider that cannot name these frameworks — or produce documentation mapped to them — is the wrong fit for a regulated Frisco firm.

What does premium IT support for a Frisco financial firm include?

Premium, financial-grade IT support combines proactive management with security and compliance built in.

  • An in-house 24/7 help desk and Security Operations Center — real engineers who know your environment, around the clock.
  • An enforced security baseline — multi-factor authentication, endpoint detection and response (EDR), and advanced email security on every user and device.
  • Immutable, restore-tested backups with a defined recovery-time objective.
  • Virtual CISO leadership — security strategy and board-ready reporting.
  • Compliance documentation — a written information security plan and audit-ready evidence mapped to SEC, FINRA, and FTC requirements.
  • Same-day on-site support across Frisco for the problems a remote session cannot solve.

The cybersecurity threats that matter most to financial firms

Financial firms are targeted because they move money and hold sensitive client data. The threats that cause the most damage:

  • Wire fraud via business email compromise (BEC) — attackers impersonate a principal, client, or vendor to redirect a transfer. Out-of-band verification on every wire is the most important control.
  • Ransomware timed to disrupt operations and pressure a payment.
  • Account takeover from stolen or reused credentials surfacing on the dark web.
  • Vendor and third-party compromise reaching your firm through a trusted connection.

Why local Frisco support matters

A genuine local presence turns IT support from a distant call center into an accountable neighbor. A Frisco-based provider can put a technician on site the same business day at offices around The Star, Frisco Station, Hall Park, Frisco Square, and the Dallas North Tollway corridor — staging equipment, running after-hours rollouts, and responding to a severity-one incident with the person who configured the environment. For a financial firm, that speed is also risk reduction. DKBinnovative also provides broader managed IT services in Frisco for firms that want full coverage.

Why DKBinnovative for Frisco financial firms

DKBinnovative has provided IT support and cybersecurity to financial services firms across Frisco and the Dallas-Fort Worth metroplex since 2004. Our model is security-first by design: an in-house 24/7 help desk and Security Operations Center, MFA and EDR enforced as standard, immutable backups, named vCISO leadership, and compliance documentation mapped to SEC Regulation S-P, FINRA, the FTC Safeguards Rule, and SOC 2. We support registered investment advisers and accounting firms with documentation built for the exams they actually face. Our help desk measured a 3-minute average first response, a 78% first-call resolution rate, and 98.14% client satisfaction in 2025.

Schedule a free IT assessment or call (888) 352-4832 to secure premium IT support for your Frisco financial firm.

Frequently Asked Questions

What should a small financial firm in Frisco look for in IT support?

Look for documented experience with SEC Regulation S-P, FINRA, and the FTC Safeguards Rule; an enforced security baseline of MFA and EDR; immutable backups; an in-house 24/7 help desk and Security Operations Center; virtual CISO leadership; and same-day on-site support in Frisco. Ask for written SLAs and audit-ready compliance documentation.

Why can’t a financial firm use a generic IT provider?

A generic provider can keep systems running but rarely produces the documented controls regulators, auditors, and cyber-insurance carriers require. A financial firm that uses one risks examination findings and uninsurable gaps. Specialist IT support builds SEC, FINRA, and FTC-aligned documentation into the engagement.

What is the biggest cybersecurity threat to a Frisco financial firm?

Wire fraud through business email compromise (BEC) is the biggest financial threat. Attackers impersonate a principal, client, or vendor to redirect a transfer. The most important control is out-of-band verification — a callback to a known number — on every wire and banking-detail change.

Does IT support for a financial firm include compliance documentation?

It should. A specialist provider produces a written information security plan and audit-ready evidence mapped to SEC Regulation S-P, FINRA, the FTC Safeguards Rule, and SOC 2 as standard scope, so the firm can answer an examiner or client questionnaire with evidence rather than scrambling.

Do you offer same-day on-site IT support in Frisco?

Yes. DKBinnovative provides same-day on-site support across Frisco — including The Star, Frisco Station, Hall Park, and the Dallas North Tollway corridor — alongside an in-house 24/7 help desk for remote support.

What frameworks does DKBinnovative support for financial firms?

DKBinnovative builds and maintains documentation mapped to SEC Regulation S-P, FINRA rules, the FTC Safeguards Rule and Gramm-Leach-Bliley, SOC 2, and the Texas SB 2610 cybersecurity safe harbor — the frameworks that matter most to Frisco financial firms.

Find Your Ideal Proactive IT Partner in Plano Today!

By DKBinnovative Team | Published: June 16, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: A proactive managed IT partner in Plano prevents problems instead of just fixing them — monitoring your systems 24/7, patching and maintaining them on a schedule, enforcing security, and planning technology around your business goals. When choosing one, look for an in-house 24/7 help desk, a built-in security baseline (MFA and EDR), a named vCIO, co-managed flexibility, same-day on-site coverage, and compliance experience for regulated firms. DKBinnovative delivers all of these as a proactive IT partner with a Plano office, headquartered in Frisco, serving Legacy West, Granite Park, the Telecom Corridor, and the wider Dallas-Fort Worth metroplex since 2004.

Key takeaways:

  • Proactive IT prevents downtime; reactive (break-fix) IT only responds after something breaks.
  • The most important sign of a proactive partner is 24/7 monitoring with a real in-house help desk.
  • Security and compliance should be built in, not sold as add-ons.
  • A named vCIO turns IT from a cost into a planned, business-aligned investment.
  • Local, same-day on-site support in Plano matters when remote fixes are not enough.

Plano is one of the strongest business communities in Texas — corporate campuses at Legacy West, fast-growing firms along the Dallas North Tollway and the Telecom Corridor, and a dense base of financial, professional, and healthcare practices. For all of them, technology is mission-critical, which is why the right IT partner has to be proactive: preventing the outages and security incidents that reactive providers only clean up afterward. This guide explains what a proactive managed IT partner actually does, how to evaluate one in Plano, and how to find your ideal fit.

What is a proactive managed IT partner?

A proactive managed IT partner manages your technology to prevent problems before they cause downtime — rather than waiting for something to break and billing you to fix it. In practice, that means round-the-clock monitoring of your servers, workstations, and network; patching and maintenance on a schedule; enforced security controls; and a technology roadmap aligned to where your business is going.

This is the opposite of the break-fix model, where you only call for help after a failure and pay per incident — which means more downtime, unpredictable costs, and security gaps. Proactive managed IT services in Plano replace that with a flat, predictable engagement built around prevention.

Why do Plano businesses need a proactive IT partner?

For a Plano business, proactive IT is the difference between a quiet, secure network and a Monday morning of outages and emergencies. Downtime stops revenue, frustrates clients, and — for the financial and professional services firms concentrated in Plano — can create compliance exposure. Proactive monitoring catches a failing drive, an expiring certificate, or a suspicious login before it becomes an outage or a breach.

It also scales. As a Plano firm grows from ten to a hundred employees, a proactive partner plans capacity, standardizes security, and keeps IT spending predictable instead of lurching from one emergency purchase to the next.

What to look for in a proactive managed IT partner in Plano

Evaluate every candidate against these seven signs of a genuinely proactive partner.

  • 24/7 monitoring and maintenance — continuous remote monitoring (RMM), scheduled patching, and health tracking that predicts failures.
  • An in-house 24/7 help desk — real engineers who know your environment answer the phone, with written response-time SLAs.
  • A built-in security baseline — MFA, endpoint detection and response (EDR), and email security included as standard, not upsells.
  • A named vCIO — a virtual CIO who owns a multi-year roadmap and runs quarterly business reviews.
  • Co-managed flexibility — the ability to support your internal IT staff rather than replace them. Explore co-managed IT.
  • Same-day on-site coverage — a local Plano presence for the problems a remote session cannot solve.
  • Compliance experience — documented work with the SEC, FINRA, FTC Safeguards Rule, HIPAA, and Texas frameworks for regulated firms.

For a deeper scorecard, see our guide to the top 10 managed IT features Plano SMBs need in 2026.

Proactive managed IT vs. reactive break-fix IT

Factor Proactive managed IT Reactive break-fix
Approach Prevents problems Reacts after failure
Downtime Minimized Frequent and costly
Cost Predictable, flat Unpredictable, per-incident
Security Continuously managed Gaps between calls
Strategy vCIO roadmap None

Plano industries and business districts we support

A strong Plano IT partner understands the local business community, not just the technology. DKBinnovative supports companies across Legacy West, Granite Park, the Telecom Corridor, and the Dallas North Tollway corridor — with particular depth in the financial, investment, accounting, legal, and healthcare firms Plano is known for. That local concentration is why financial services IT and compliance are core to how we deliver proactive support here.

Why DKBinnovative is your ideal proactive IT partner in Plano

DKBinnovative has delivered proactive managed IT services in Plano since 2004. Our model is proactive by design: 24/7 monitoring and an in-house help desk and Security Operations Center, MFA and EDR enforced as standard, named vCIO leadership, co-managed flexibility, same-day on-site support, and compliance documentation built for regulated Plano firms. Our help desk measured a 3-minute average first response, a 78% first-call resolution rate, and 98.14% client satisfaction in 2025 — the kind of numbers a proactive partner can actually show you. Need a technician on site fast? We also provide same-day on-site IT support in Plano.

Schedule a free IT assessment or call (888) 352-4832 to find your ideal proactive IT partner in Plano today.

How to choose a strategic managed IT partner?

A strategic partner plans around where the business is heading; a vendor closes tickets. Test for it directly: ask when you last reviewed a technology roadmap together, who your named strategic contact is, and how technology decisions get tied to budget. If nobody owns that conversation, it is not a partnership.

Frequently Asked Questions

What is a proactive managed IT partner?

A proactive managed IT partner manages your technology to prevent problems before they cause downtime — monitoring systems 24/7, patching and maintaining them on a schedule, enforcing security, and planning technology around your business goals — rather than only fixing issues after they break.

How is proactive managed IT different from break-fix IT?

Proactive managed IT uses continuous monitoring and a flat monthly fee to prevent issues, while break-fix IT is reactive: you call after something fails and pay per incident. Proactive IT means less downtime, predictable costs, and continuously managed security.

How do I choose a proactive IT partner in Plano?

Look for 24/7 monitoring with an in-house help desk, a built-in security baseline (MFA and EDR), a named vCIO, co-managed flexibility, same-day on-site coverage in Plano, and documented compliance experience if your firm is regulated. Ask each provider for written SLAs and recent performance metrics.

Does a proactive IT partner include cybersecurity?

Yes. A genuinely proactive partner builds security in — multi-factor authentication, endpoint detection and response, email security, and continuous monitoring — as standard scope rather than as separate add-ons, because prevention and security are the same discipline.

Can a proactive IT partner work alongside our internal IT team?

Yes. A co-managed IT model lets the partner support your internal staff — adding 24/7 coverage, security operations, and specialist depth — while your team keeps day-to-day ownership. The best partners define the responsibility split in writing.

Why choose a local Plano IT partner?

A local partner can provide same-day on-site support, understands the Plano business community, and is accountable in a way a distant national vendor is not. For hands-on problems, office moves, or urgent incidents, local presence eliminates an entire category of delay.

Unlock Success: Discover the Leading IT Companies for Private Equity in Dallas

By DKBinnovative Team | Published: June 16, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: The leading IT companies for private equity in Dallas are the providers that go beyond help desk and deliver what PE firms actually need: cybersecurity due diligence before a deal closes, security standardization across portfolio companies, SEC-aligned compliance, data-room and wire-transfer protection, virtual CISO leadership, and IT as a value-creation lever from acquisition to exit. DKBinnovative delivers all of these for private equity sponsors and portfolio companies across Dallas, Plano, Frisco, and Irving, and has done so since 2004.

Key takeaways:

  • PE firms are high-value targets because they move large sums and hold sensitive deal data.
  • The biggest deal-stage threat is wire fraud via business email compromise (BEC).
  • The best IT partners support the full PE lifecycle: due diligence, the 100-day plan, value creation, and exit.
  • Cybersecurity is now a value lever and an exit-readiness factor, not just a cost.
  • Dallas-Fort Worth is a major PE hub, so local, accountable IT support is an advantage.

Dallas-Fort Worth is one of the country’s most active private equity centers — home to firms such as TPG in Fort Worth, NGP in Irving, and Trive Capital, Hudson Advisors, and Tailwater Capital in Dallas, alongside dozens of smaller sponsors and hundreds of portfolio companies across the metroplex. Those firms and the businesses they own run on technology and live or die by data security. Choosing the right IT company is therefore not a back-office decision; it shapes deal velocity, portfolio value, and exit multiples. This guide explains what the leading IT companies for private equity in Dallas actually deliver, and how to choose one.

Why do private equity firms need specialized IT and cybersecurity?

Private equity firms combine large, time-pressured money movements with highly sensitive deal data — a profile that makes them prime targets and raises the bar on IT. A PE sponsor moves capital on tight closing timelines, shares confidential information through virtual data rooms, registers with the SEC as an investment adviser, and is ultimately accountable for the security posture of every company in its portfolio. A generic managed IT provider that has never supported a deal will not anticipate any of this.

Specialized IT support for private equity protects the firm at the fund level and standardizes security across portfolio companies — turning cybersecurity from a recurring risk into a measurable part of value creation.

What makes the best IT company for a private equity firm?

Evaluate providers on the capabilities that match how a PE firm actually operates.

  • Cybersecurity due diligence — assessing a target’s security and IT risk before the deal closes, so liabilities are priced in.
  • Portfolio standardization — a repeatable security baseline (MFA, EDR, backup, monitoring) deployed across every portfolio company.
  • SEC and regulatory alignment — support for Regulation S-P, the Marketing Rule, books-and-records, and exam readiness at the management-company level.
  • Deal and data-room security — protecting confidential information and verifying every wire and banking change.
  • Virtual CISO leadership — executive security strategy and reporting for the fund and its boards.
  • Value creation and exit readiness — documented security that survives buyer due diligence and supports the multiple.
  • Local, accountable support — managed IT and on-site coverage across Dallas, Plano, Frisco, and Irving.

IT across the private equity lifecycle

Our service page for managed IT for private equity portfolio companies breaks each stage down in detail.

The best IT companies for private equity engage at every stage of the deal, not just after close.

  • Pre-deal — cyber due diligence: assess the target’s security posture, identify breach history and unpatched risk, and quantify remediation cost before signing.
  • First 100 days — integration: deploy the security baseline, consolidate identity in Microsoft 365 and Microsoft Azure, and close the gaps the diligence surfaced.
  • Hold period — value creation: run the portfolio company on proactive managed IT, reduce downtime, and report security posture to the board.
  • Exit — readiness: produce the documented security and compliance evidence a buyer’s diligence team will demand, protecting the valuation.

Our DFW private equity cyber due diligence and value-creation playbook details this four-phase approach.

The cybersecurity threats that matter most to PE firms

Deal activity attracts attackers, and the most damaging threats cluster around transactions.

  • Wire fraud via business email compromise (BEC): attackers impersonate a partner, seller, or attorney to redirect a closing wire — the single largest financial threat to a PE firm.
  • Data-room and confidential-information exposure: leaked deal data damages negotiations and reputation.
  • Event-timed ransomware: attacks launched around a close or liquidity event, when pressure to pay peaks.
  • Portfolio-company breaches: a single weak portfolio company can create fund-level reputational and financial damage.

The most important single control is out-of-band verification — a callback to a known number — on every wire and banking-detail change.

How to choose an IT company for your Dallas PE firm

Use this checklist when comparing providers.

  1. Documented experience supporting PE firms and portfolio companies — not generic small-business IT.
  2. A repeatable cyber due diligence process you can deploy on a target in days.
  3. A standardized security baseline (MFA, EDR, backup, 24/7 monitoring) for portfolio rollout.
  4. SEC and Regulation S-P experience at the management-company level.
  5. Specific wire-fraud and BEC controls, including out-of-band verification.
  6. Virtual CISO leadership and board-ready reporting.
  7. A genuine local presence with managed IT and on-site support across Dallas, Plano, Frisco, and Irving.

Why DKBinnovative for Dallas-area private equity firms

DKBinnovative provides managed IT, cybersecurity, and compliance for private equity sponsors and their portfolio companies across the Dallas-Fort Worth metroplex, and has done so since 2004. We deliver cyber due diligence before a deal closes, a standardized security baseline for portfolio rollout, virtual CISO leadership, and SEC- and Regulation S-P-aligned documentation — all backed by an in-house 24/7 Security Operations Center and a help desk that measured a 3-minute average first response and 98.14% client satisfaction in 2025. Portfolio companies get proactive managed IT services in Plano, Frisco, and Irving, with same-day on-site coverage and secure AI adoption through Hatz.AI.

Schedule a confidential consultation or call (888) 352-4832 to discuss cyber due diligence or portfolio IT for your Dallas private equity firm.

Frequently Asked Questions

What should a private equity firm look for in an IT company?

A PE firm should look for cybersecurity due diligence capability, a standardized security baseline for portfolio companies, SEC and Regulation S-P experience, deal and data-room protection, virtual CISO leadership, and a local presence with managed IT and on-site support across Dallas, Plano, Frisco, and Irving.

What is cybersecurity due diligence in private equity?

Cybersecurity due diligence is the assessment of a target company’s security posture and IT risk before an acquisition closes — identifying breach history, unpatched vulnerabilities, compliance gaps, and remediation costs so the buyer can price the risk and plan the first 100 days.

Why are private equity firms targeted by cybercriminals?

PE firms move large sums on tight timelines and hold confidential deal data, which makes them attractive targets for wire fraud and data theft. Business email compromise — impersonating a partner, seller, or attorney to redirect a closing wire — is the most common and costly attack.

How does IT create value in a private equity portfolio?

Strong IT reduces portfolio-company downtime, standardizes security to lower fund-level risk, and produces documented compliance that survives buyer due diligence at exit — protecting and often improving the valuation multiple. Cybersecurity has shifted from a cost to a measurable value lever.

Do private equity firms have to comply with SEC cybersecurity rules?

Most private equity advisers register with the SEC and are subject to expectations including Regulation S-P safeguards, books-and-records rules, and the Marketing Rule. A specialized IT partner helps the management company maintain the documentation and controls an SEC examination evaluates.

Does DKBinnovative support PE portfolio companies across DFW?

Yes. DKBinnovative provides managed IT services and cybersecurity for private equity portfolio companies across Dallas, Plano, Frisco, and Irving, with same-day on-site support, a standardized security baseline, and virtual CISO leadership for the fund.


Published June 16, 2026 by the DKBinnovative Team. Reviewed by Peter Bertran, Chief Client Officer. DKBinnovative is a managed IT, cybersecurity, and virtual CISO firm serving private equity, financial, and professional services firms across the Dallas-Fort Worth metroplex since 2004. Firm names are referenced for context only and do not imply any relationship or endorsement. This article is educational and is not legal or investment advice.

Elevate Your Security: Virtual CISO Services Tailored for DFW Family Offices

By DKBinnovative Team | Published: June 11, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: A virtual CISO (vCISO) gives a family office executive-level security leadership — strategy, governance, risk management, and incident response — without the cost of a full-time chief information security officer. For sophisticated DFW family offices, the right vCISO builds a security program around the office’s unique exposure: large wire transfers, vendor impersonation, principals’ privacy, household staff, multiple residences, and smart-home technology — aligned to NIST CSF and CIS Controls, and to SEC and GLBA obligations where the office manages investments or financial accounts.

Key takeaways:

  • A vCISO delivers CISO-level strategy and accountability on a fractional basis.
  • Family offices are high-value targets because they combine great wealth with lean security staffing.
  • The top threat is wire/payment fraud via business email compromise (BEC) and vendor impersonation.
  • Protection must extend beyond the office to principals, household staff, residences, and personal devices.
  • A credible vCISO works within recognized frameworks (NIST CSF, CIS Controls, SOC 2) and any SEC/GLBA duties.

A family office concentrates extraordinary wealth, sensitive personal information, and high-value transactions inside a small, relationship-driven team — an irresistible target for attackers, and rarely one with a full-time security executive. A virtual CISO closes that gap. This guide explains what a vCISO does for a sophisticated DFW family office, the specific risks the role addresses, the frameworks it works within, and how to choose the right provider.

What is a virtual CISO (vCISO), and why do family offices need one?

A virtual CISO is an experienced security executive who leads a family office’s security program on a fractional, ongoing basis — setting strategy, owning governance and risk, and directing incident response — without the expense of a full-time hire. Most family offices run lean: a handful of professionals managing investments, accounting, property, travel, and philanthropy. They have the risk profile of a financial institution but rarely the security leadership of one.

A vCISO supplies that leadership: a named expert accountable for the office’s security posture, who translates threats into decisions the principals and staff can act on, and who can stand in front of the family, the board, or an auditor with a clear plan.

Why are family offices high-value cyber targets?

Family offices pair enormous financial capacity with limited internal security — the combination attackers prize most. The specific exposures a vCISO is built to address:

  • Wire and payment fraud (BEC): family offices move large sums on tight timelines, making business email compromise and fraudulent payment-redirection the single biggest financial threat.
  • Vendor and advisor impersonation: attackers compromise or spoof a trusted attorney, accountant, or contractor to authorize transfers or extract data.
  • AI-enabled voice and email mimicry: deepfake audio and AI-written messages now impersonate principals to pressure staff into urgent payments.
  • Principal and family privacy: data-broker exposure, doxxing, and social-media reconnaissance that enable both cyber and physical threats.
  • Household staff and personal devices: assistants, estate managers, and family members are frequent entry points, often outside any corporate security controls.
  • Multiple residences and smart homes: home networks, Wi-Fi, and IoT/smart-home devices that are rarely hardened or monitored.
  • Account takeover and credential theft: reused or exposed passwords surfacing on the dark web.
  • Event-timed ransomware: attacks launched around liquidity events, closings, or travel, when pressure to pay is highest.

What does a vCISO do for a family office?

A family-office vCISO owns the full security program, not a single tool. The core scope:

  • Security strategy and roadmap tailored to the office’s wealth profile, entities, and risk tolerance.
  • Risk assessments across the office, principals, residences, and key vendors.
  • Governance and policy — acceptable use, payment-authorization controls, travel and device policies.
  • Payment-fraud controls — out-of-band verification (callback) procedures for every wire and vendor banking change.
  • Incident response planning with tabletop exercises so staff rehearse a fraud or breach before it happens.
  • Third-party and vendor risk management for the attorneys, accountants, and managers the office relies on.
  • Security awareness for principals, family members, and household staff — in plain language, with discretion.
  • Reporting to the family and the board, translating posture into clear, non-technical terms.
  • Regulatory liaison where the office is a registered or exempt reporting adviser, or otherwise subject to SEC and GLBA expectations.

vCISO vs. a full-time CISO vs. an MSSP

For most family offices, a vCISO is the right fit because it delivers senior leadership at a fraction of a full-time hire’s cost, with broader experience than one person could offer.

Model What it provides Best fit
Virtual CISO (vCISO) Fractional executive security leadership, strategy, governance, and oversight Most family offices
Full-time CISO Dedicated in-house executive Very large offices with constant, complex needs
MSSP only Outsourced monitoring and tooling, but no strategic ownership Offices that already have leadership and need execution

The strongest arrangement pairs a vCISO for strategy and accountability with a managed security operations team for 24/7 execution — leadership and hands working together.

What frameworks and compliance does a family-office vCISO work within?

A credible vCISO builds the program on recognized standards rather than ad-hoc fixes. The ones that matter for family offices:

  • NIST Cybersecurity Framework (CSF) and CIS Controls — the backbone for assessing and prioritizing safeguards.
  • SOC 2 — relevant when the office relies on vendors that should hold an attestation, and as a model for its own controls.
  • SEC expectations — where the family office is a registered investment adviser or exempt reporting adviser, including Regulation S-P safeguards.
  • Gramm-Leach-Bliley Act (GLBA) and the FTC Safeguards Rule — where the office handles financial accounts and nonpublic personal information.
  • State privacy obligations — protecting the personal data of principals and family members.

How to choose a vCISO for your family office

Evaluate providers against criteria that match a family office’s discretion and risk profile.

  • Demonstrated experience with family offices, wealth managers, or financial firms — not generic IT.
  • A documented approach mapped to NIST CSF or CIS Controls.
  • Specific payment-fraud and BEC controls, including out-of-band verification procedures.
  • Protection that extends to principals, family, household staff, and residences.
  • A 24/7 Security Operations Center (SOC) or MDR partner for execution behind the strategy.
  • Discretion, confidentiality, and references that respect privacy.
  • Clear, non-technical reporting the family and board will actually use.

Why DKBinnovative for DFW family offices

DKBinnovative provides virtual CISO services and cybersecurity for family offices, wealth managers, and financial services firms across Dallas-Fort Worth, and has done so since 2004. Our vCISO engagements pair executive security leadership — strategy, governance, payment-fraud controls, vendor risk, and family-and-staff awareness — with an in-house 24/7 Security Operations Center for round-the-clock execution. We build programs on the NIST CSF and CIS Controls, support SEC and GLBA obligations where the office manages investments, and help families adopt AI safely through Hatz.AI as a secure AI platform. Our in-house help desk measured a 3-minute average first response and 98.14% client satisfaction in 2025.

Schedule a private consultation or call (888) 352-4832 to discuss a vCISO engagement for your DFW family office.

Frequently Asked Questions

What is a virtual CISO for a family office?

A virtual CISO (vCISO) is an experienced security executive who leads a family office’s cybersecurity program on a fractional basis — setting strategy, managing risk and governance, and directing incident response — without the cost of a full-time chief information security officer.

Why do family offices need a vCISO?

Family offices combine significant wealth and large transactions with small teams and little in-house security leadership. A vCISO provides the executive-level oversight needed to defend against wire fraud, vendor impersonation, and privacy threats that target principals and staff.

What is the biggest cybersecurity threat to a family office?

Wire and payment fraud through business email compromise (BEC) is the biggest financial threat. Attackers impersonate a principal, advisor, or vendor to redirect a large transfer. Out-of-band verification (a callback to a known number) on every wire and banking change is the most important control.

How is a vCISO different from a full-time CISO or an MSSP?

A vCISO delivers fractional executive leadership and strategy; a full-time CISO is a dedicated in-house hire suited to very large offices; an MSSP provides outsourced monitoring and tools but not strategic ownership. Most family offices are best served by a vCISO paired with a managed security operations team.

Does a family office have to comply with SEC or GLBA rules?

It depends on structure. A family office that is a registered or exempt reporting investment adviser faces SEC expectations, including Regulation S-P. An office that handles financial accounts and nonpublic personal information may fall under GLBA and the FTC Safeguards Rule. A vCISO helps determine and meet these obligations.

Does vCISO protection cover principals’ homes and personal devices?

It should. A family office’s real attack surface includes principals, family members, household staff, multiple residences, home networks, and smart-home devices. A strong vCISO program extends governance and protection beyond the office to these personal environments.


Published June 11, 2026 by the DKBinnovative Team. Reviewed by Peter Bertran, Chief Client Officer. DKBinnovative is a managed IT, cybersecurity, and virtual CISO firm serving family offices, financial, and professional services firms across the Dallas-Fort Worth metroplex since 2004. This article is educational and is not legal or compliance advice.

Maximize Efficiency: The Best IT Companies for Accounting Solutions

By DKBinnovative Team | Published: June 11, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: The best IT companies for accounting solutions are the providers that combine deep accounting-software expertise (QuickBooks, Lacerte, UltraTax CS, Drake, CCH Axcess, ProSystem fx, Sage), built-in security and compliance for the FTC Safeguards Rule and IRS Publication 4557, tax-season-grade uptime, fast response with measured SLAs, flexible cloud hosting, transparent pricing, and verifiable client proof. DKBinnovative is a specialized accounting-IT provider with offices in Frisco, Plano, and Irving that delivers all seven, with a written information security plan (WISP) and SOC-ready documentation as standard scope.

Key takeaways:

  • The single biggest differentiator is accounting-application expertise — generalist IT shops slow firms down at the worst time.
  • Under Gramm-Leach-Bliley, accounting firms are “financial institutions,” so the FTC Safeguards Rule and IRS Publication 4557 make security a legal duty.
  • Tax-season uptime and fast, measured response times matter more for accounting than almost any other industry.
  • A real provider includes a WISP, MFA, EDR, immutable backups, and a 24/7 SOC as standard — not as upsells.
  • Evaluate the field against the seven weighted criteria below before signing.

Accounting and tax firms run on specialized software, sensitive client financial data, and deadlines that do not move. That makes choosing an IT company one of the most consequential vendor decisions a firm makes — the wrong partner means slow tax-season support, compliance gaps an examiner can find, and downtime when the firm can least afford it. This guide explains what separates the best IT companies for accounting solutions, the criteria to score providers on, and how to verify each claim before you sign.

What makes the best IT company for accounting solutions?

The best IT companies for accounting firms are defined by seven measurable capabilities — not by marketing. Use these as a weighted scorecard when comparing providers; the weights reflect what actually protects an accounting practice’s revenue, clients, and compliance posture.

  • Accounting application expertise (25%) — hands-on support for the tax and accounting stack, not just “Windows and email.”
  • Security & compliance (20%) — FTC Safeguards Rule, IRS Publication 4557, WISP, and SOC 2 readiness built in.
  • Uptime & peak-season performance (15%) — the environment stays up through filing deadlines.
  • Response time & resolution (15%) — written SLAs with published, measured performance.
  • Cloud & hosting flexibility (10%) — secure hosting for the firm’s applications and data, on the model that fits.
  • Pricing transparency & contracts (10%) — a clear, predictable per-user model with scope in writing.
  • Customer proof & reviews (5%) — verifiable references and accounting-firm case studies.

A provider that scores well on the first two categories — application expertise and compliance — will almost always be the right fit for an accounting firm, because those are the two things generalist IT companies get wrong most often.

Which accounting platforms should your IT provider support?

Your IT provider should already run the platforms your practice depends on — configuration, performance tuning, updates, and hosting — without a learning curve on your time. This is a question about provider capability, not about which software your firm should buy. When you evaluate a provider, confirm hands-on depth with the platforms you already run:

  • Tax: UltraTax CS, Lacerte, ProSeries, Drake Tax, CCH Axcess, ProSystem fx, TaxAct
  • Accounting & bookkeeping: QuickBooks Desktop and Enterprise, QuickBooks Online, Sage 50, Sage Intacct
  • Workflow & documents: SmartVault, Bill.com, Expensify, Gusto, practice-management and document-management systems

The difference shows up under load. A provider that knows how QuickBooks Enterprise behaves in a hosted multi-user environment, or how UltraTax handles network file locking during e-file season, resolves problems in minutes. A generalist learns on your busiest week.

What security and compliance must the best providers build in?

Because accounting firms are “financial institutions” under Gramm-Leach-Bliley, data protection is a legal duty — and the right IT company treats it as standard scope. The controls that matter:

  • FTC Safeguards Rule — a written information security program with access controls, encryption, vendor oversight, and monitoring.
  • IRS Publication 4557 — a maintained written information security plan (WISP), effectively required for firms with a PTIN.
  • SOC 2 — the provider should hold its own SOC 2 attestation and help the firm produce control evidence.
  • Core security stack — multi-factor authentication (MFA), endpoint detection and response (EDR), email security, SIEM monitoring, and immutable, restore-tested backups, watched by a 24/7 Security Operations Center (SOC).

Ask whether each of these is included in the base engagement or sold as a tier above it. With cyber-insurance carriers and the IRS treating these as table stakes, a provider that line-items core security is the wrong fit.

The 12-point IT compliance checklist for accounting firms

The best IT companies for accounting firms can produce evidence for all twelve of these controls on request. Use it to test any provider:

  1. A current Written Information Security Plan (WISP) tailored to the firm (IRS Publication 4557).
  2. A designated security coordinator named in writing (FTC Safeguards Rule).
  3. Multi-factor authentication enforced on email, remote access, and all administrator accounts.
  4. Endpoint detection and response (EDR) on every workstation and server.
  5. Encryption of taxpayer data both at rest and in transit.
  6. Advanced email security and anti-phishing protection.
  7. 24/7 SOC or MDR monitoring with SIEM log collection.
  8. Immutable, off-network, restore-tested backups with a defined recovery-time objective.
  9. Documented access controls with least-privilege, role-based permissions.
  10. Third-party and vendor risk oversight.
  11. A written incident-response plan with breach-notification procedures.
  12. An annual risk assessment and documented security-awareness training.

What types of IT companies serve accounting firms?

The market splits into four categories, and the best choice depends on your firm’s size, software, and compliance profile.

  • National application-hosting specialists (for example, Rightworks or Verito) — host your tax and accounting software in their cloud. Strong for hosting, but often thinner on broader managed IT, on-site support, and firm-specific compliance work.
  • National accounting-focused MSPs (for example, Nerds Support) — broad managed IT with accounting-vertical knowledge, but support can feel impersonal and far from your office.
  • Regional specialized MSPs — managed IT firms with genuine accounting and financial-services depth plus a local presence. This category fits most small and mid-sized firms best, because it combines vertical expertise, compliance documentation, and accountable, nearby support. DKBinnovative sits here.
  • Generalist MSPs — competent at basic IT but without accounting-software or compliance depth; usually the weakest fit for a regulated firm.

How the categories compare on the factors that matter most to an accounting firm:

Provider type Accounting-software depth Compliance docs (WISP/FTC/4557) Local / on-site support Best fit
National hosting specialist High (hosting) Partial Limited Firms wanting cloud hosting only
National accounting MSP Medium–High Yes Remote-first Larger multi-state firms
Regional specialized MSP High Yes (standard scope) Same-day on-site Most small & mid-sized firms
Generalist MSP Low Rarely Varies Non-regulated small business

A buyer’s checklist for accounting firms

Before you sign with any IT company, confirm each of these in writing.

  • Documented, hands-on expertise with your specific tax and accounting software.
  • A WISP and FTC Safeguards-aligned security program as standard scope.
  • The provider’s own SOC 2 report available on request.
  • MFA, EDR, email security, SIEM, and immutable backups included by default.
  • Written response-time SLAs plus last-quarter performance metrics.
  • A tax-season uptime and support plan, with a defined recovery-time objective.
  • Transparent per-user pricing with scope in writing — no surprise tier-ups.
  • Accounting-firm references and a documented onboarding timeline.

What onboarding with a top accounting IT company looks like

A strong provider moves a firm from contract to full coverage in a documented 45-to-90-day plan with no gap in support. The phases:

  • Phase 1 — Discovery & assessment (weeks 1–2): inventory applications and data, baseline security, and run a compliance gap analysis against the FTC Safeguards Rule and IRS Publication 4557.
  • Phase 2 — Secure deployment & migration (weeks 2–6): roll out MFA, EDR, email security, and immutable backups; migrate or stabilize hosted accounting and tax software with coverage overlap so nothing goes dark.
  • Phase 3 — Compliance documentation (weeks 4–8): produce the WISP, access and incident-response policies, and an audit-ready evidence record.
  • Phase 4 — Optimization & review: tune performance for tax-season load and set a quarterly business-review cadence with a named strategic lead.

Ask any candidate provider to show this plan in writing before you sign — the best IT companies for accounting already have one.

Best IT companies for accounting firms in Plano, Frisco, and Irving

For CPA and accounting firms in Plano, Frisco, and Irving, the strongest fit is a regional specialized MSP with offices in the corridor, because tax-season problems need someone on site the same day. National hosting providers cover the software but not the office. Generalist local shops cover the office but not UltraTax, CCH Axcess, or a WISP.

DKBinnovative is headquartered in Frisco, with offices in Plano and Irving (Las Colinas). Accounting firms across Collin and Dallas counties get same-day on-site response, help desk staff who already support UltraTax CS, CCH Axcess, Lacerte, Drake, and QuickBooks, and a WISP aligned to IRS Publication 4557 and the FTC Safeguards Rule as standard scope.

Why DKBinnovative is a top choice for accounting IT

DKBinnovative is a specialized provider of managed IT for accounting and CPA firms, supporting financial and professional services firms across Frisco, Plano, Irving, and the rest of DFW since 2004. We are built for the seven criteria above: native support for QuickBooks, UltraTax CS, Lacerte, Drake, CCH Axcess, ProSystem fx, and Sage; a WISP and FTC Safeguards- and IRS Publication 4557-aligned compliance program as standard scope; MFA, EDR, email security, and immutable backups watched by an in-house 24/7 Security Operations Center; tax-season-grade uptime; written SLAs; and transparent per-user pricing. Our in-house help desk measured a 3-minute average first response, a 78% first-call resolution rate, and 98.14% client satisfaction in 2025.

For firms weighing how to govern new tools safely, we also help accounting practices adopt AI compliantly — see our guide on AI for accounting and CPA firms under IRS 4557 and the FTC Safeguards Rule.

Schedule a free IT assessment or call (888) 352-4832 to score DKBinnovative against the seven criteria for your firm.

Frequently Asked Questions

What is the best IT support for an accounting firm?

The best IT support for an accounting firm comes from a provider with deep expertise in tax and accounting software (such as QuickBooks, UltraTax CS, Lacerte, Drake, and CCH Axcess), built-in compliance for the FTC Safeguards Rule and IRS Publication 4557, tax-season-grade uptime, written response-time SLAs, secure cloud hosting, and verifiable client references.

What is the difference between an IT MSP and an application-hosting provider for accounting firms?

A hosting provider runs your accounting and tax applications in its cloud. A managed IT services provider (MSP) manages your entire IT environment — help desk, security, compliance, networks, and devices — and may also host applications. Accounting firms that need security, compliance documentation, and full support are usually better served by a specialized MSP.

Does the FTC Safeguards Rule apply to small accounting firms?

Yes. Under Gramm-Leach-Bliley, tax and accounting firms are financial institutions, so the FTC Safeguards Rule applies regardless of firm size. It requires a written information security program with access controls, encryption, vendor oversight, monitoring, and a designated person accountable for it.

What is a WISP and does my accounting firm need one?

A WISP is a Written Information Security Plan describing how a firm protects client and taxpayer data. IRS Publication 4557 makes a WISP effectively mandatory for firms with a Preparer Tax Identification Number (PTIN). The best IT providers create and maintain it as part of the engagement rather than as a separate project.

What security controls should an accounting firm’s IT provider include?

At minimum: multi-factor authentication (MFA), endpoint detection and response (EDR), advanced email security, SIEM monitoring, immutable and restore-tested backups, and a 24/7 Security Operations Center — all included as standard scope, not priced as separate upgrades.

How do the best IT companies handle accounting tax season?

They plan for it: hardened uptime with a defined recovery-time objective, capacity for peak multi-user load on hosted tax software, priority response SLAs during filing season, and staff trained before the season starts rather than during it.

How should an accounting firm switch IT providers without disruption?

Choose a provider with a documented onboarding plan and a defined timeline — typically 45 to 90 days — that includes discovery, secure migration of applications and data, security and compliance baselining, and a coverage overlap so there is no gap in support during the transition.

Who provides managed IT for accounting firms in Plano?

DKBinnovative provides managed IT for CPA and accounting firms in Plano, Frisco, and Irving from offices in all three cities. Support covers UltraTax CS, CCH Axcess, Lacerte, Drake, and QuickBooks, with a WISP and FTC Safeguards-aligned security program as standard scope and same-day on-site response.


Published June 11, 2026 by the DKBinnovative Team. Reviewed by Peter Bertran, Chief Client Officer. DKBinnovative is a managed IT and cybersecurity firm supporting accounting, financial, and professional services firms since 2004. This article is educational and is not legal or compliance advice.

AI for DFW Law Firms: Using AI Without Breaching Client Confidentiality

By DKBinnovative Team | Published: June 11, 2026 | Reviewed by Peter Bertran, Chief Client Officer

Quick answer: DFW law firms can use AI, but the duty of confidentiality (ABA Model Rule 1.6) and competence (Rule 1.1) mean it has to be governed. Entering client-confidential information into a public consumer AI tool risks an unauthorized disclosure. The compliant path is a firm-controlled secure-AI platform that keeps matter data inside the firm, with access controls, logging, a written AI policy, and lawyer supervision of the output (Rule 5.3).

Key takeaways:

  • ABA Formal Opinion 512 (2024) confirms lawyers may use generative AI — with confidentiality, competence, and supervision duties intact.
  • Pasting client-confidential data into public AI risks violating Model Rule 1.6.
  • Lawyers must supervise and verify AI output; AI does not transfer professional responsibility.
  • A governed secure-AI platform keeps matter data inside the firm.
  • A written AI use policy and staff training are now table stakes.

AI is changing legal practice — drafting, document review, research, and discovery are all faster with it. Across Dallas-Fort Worth, firms from solo practices to mid-sized litigation shops are adopting AI. But a lawyer’s duty of confidentiality is near-absolute, and client matter data is exactly what a public AI tool may retain or expose. The question every managing partner is weighing: how do we use AI without breaching client confidentiality?

Here is the governed path for a DFW law firm, mapped to the ethics rules that actually apply.

Can lawyers ethically use AI?

Yes — ABA Formal Opinion 512 (2024) confirms lawyers may use generative AI, provided they uphold confidentiality, competence, communication, and supervision duties. AI is a tool, not a delegation of professional responsibility. The opinion makes clear that the lawyer remains accountable for the work product and must understand the tool’s benefits and risks well enough to use it competently under Model Rule 1.1.

So the question is not whether a firm may use AI, but whether it has put the right guardrails around it.

How does AI threaten client confidentiality?

The main threat is client-confidential information entered into a public AI tool that may store or reuse it. Model Rule 1.6 requires a lawyer to make reasonable efforts to prevent unauthorized disclosure of information relating to a client’s representation. When an associate pastes a contract, a deposition excerpt, or matter facts into a free consumer chatbot, that information leaves the firm with no obligation of confidentiality — a disclosure the rule was written to prevent.

For litigation and transactional work alike, ethical walls and matter confidentiality cannot be enforced if the data has already left the building through an ungoverned tool.

What does a competent, supervised AI workflow require?

Lawyers must verify AI output and supervise its use — AI does not lower the standard of care. Model Rule 1.1 (competence) and Rule 5.3 (supervision of nonlawyer assistance) mean a firm must:

  • Verify AI-generated research and citations — courts have sanctioned lawyers for fabricated, AI-“hallucinated” cases.
  • Supervise how staff use AI, with clear policies on approved tools and tasks.
  • Understand, at a working level, how the firm’s AI tools handle data.
  • Consider client communication and consent where relevant to the engagement.

How do law firms deploy AI without breaching confidentiality?

Give lawyers and staff a firm-controlled AI platform so matter data never leaves the firm. The compliant path has five parts:

  • Use a secure-AI control layer. DKBinnovative deploys Hatz.AI as a secure AI platform that keeps prompts and matter data inside the firm rather than a public model.
  • Control identity and access through Microsoft 365 and Microsoft Azure — single sign-on, conditional access, and permissions that respect ethical walls.
  • Log and monitor usage with data-loss-prevention rules that flag confidential data leaving approved boundaries.
  • Adopt a written AI use policy naming approved tools, prohibited data, and the verification step before AI output is relied on.
  • Train every timekeeper on confidentiality, hallucination risk, and supervision duties.

It is the same governed model DKBinnovative built in our secure AI deployment for investment firms — adapted to legal ethics rules.

An AI-readiness checklist for DFW law firms

  • Approved AI tools keep matter data inside the firm; public tools are off-limits for client data.
  • A written AI use policy is adopted, distributed, and acknowledged.
  • Access controls respect ethical walls and matter-level confidentiality.
  • A verification step is required before AI research or citations are used.
  • AI usage is logged and monitored with data-loss prevention.
  • Every timekeeper is trained on confidentiality and supervision duties.
  • A named owner is accountable for AI governance.

How DKBinnovative helps DFW law firms adopt AI safely

DKBinnovative has delivered managed IT for law firms across Dallas-Fort Worth since 2004. We give firms a governed path to AI: a firm-controlled secure-AI platform, Microsoft 365 and Azure identity controls that respect ethical walls, audit logging and data-loss prevention, and a written AI use policy mapped to ABA Model Rules 1.1, 1.6, and 5.3 — backed by cybersecurity and compliance documentation built for the confidentiality standard your clients expect.

Schedule a free AI readiness assessment or call (888) 352-4832 to map a confidentiality-safe AI rollout for your DFW law firm.

Related reading: the same governed approach for other regulated DFW firms — HIPAA-compliant AI for DFW healthcare practices and AI for DFW accounting & CPA firms.

For the complete framework, see our AI governance policy guide – the SEC-ready template professional-services firms use to document AI oversight, supervision, and recordkeeping.

Frequently Asked Questions

Can lawyers use ChatGPT for legal work?

Lawyers may use generative AI under ABA Formal Opinion 512, but not by entering client-confidential information into the free consumer version, which can retain or reuse it and risk violating Model Rule 1.6. Client work should run through a firm-controlled platform that keeps matter data inside the firm, with lawyer verification of the output.

Does using AI violate attorney-client confidentiality?

It can, if client-confidential information is entered into a tool that may store or reuse it. Model Rule 1.6 requires reasonable efforts to prevent unauthorized disclosure. Using a governed, firm-controlled AI platform with access controls and logging keeps the information protected.

Do we need a written AI policy for our law firm?

Yes. A written AI use policy that names approved tools, prohibits entering client data into others, and requires verification of AI output is now a practical necessity — it supports your competence and supervision duties under Model Rules 1.1 and 5.3 and gives staff clear guardrails.

What happens if AI generates a fake case citation?

The lawyer is responsible. Courts have sanctioned attorneys who filed briefs with fabricated, AI-generated citations. Competence under Model Rule 1.1 requires verifying every AI-produced authority before it is relied on or filed.

How do we let associates and staff use AI safely?

Provide an approved secure-AI platform that keeps matter data inside the firm, enforce access controls and logging, require verification of output, and train every timekeeper. A sanctioned tool removes the temptation to use risky public chatbots for client work.


Published June 11, 2026 by the DKBinnovative Team. Reviewed by Peter Bertran, Chief Client Officer. DKBinnovative is a Frisco-based managed IT and cybersecurity firm supporting law firms and professional services firms across the Dallas-Fort Worth metroplex since 2004. This article is educational and is not legal or compliance advice.

Sales & Support
(888) 352-4832