By the DKBinnovative Crew | Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
Quick answer: Microsoft 365 Copilot respects your existing permissions: it can only use files, emails and chats a user already has access to. That makes it exactly as safe as your permissions are. At most professional firms, years of loose sharing mean Copilot can surface client files to people who should never see them. Fix permissions first, write a short AI policy, then pilot.
What Copilot can actually see
Copilot works across Outlook, Teams, Word, Excel and SharePoint. When a user asks it a question, it searches everything that user is allowed to open. It does not break permissions. It makes them visible.
That is the problem. A folder shared with “Everyone” in 2019 was hard to find before. With Copilot, a staff member can ask to see salary information or summarize a client estate file and get an answer if the permissions allow it.
Fix oversharing first
Before you buy a single license:
Find “Everyone” and “anyone with the link” shares in SharePoint and OneDrive, and remove them from client folders.
Lock down HR, partner and finance folders to the people who need them.
Check Teams and old project sites that no one owns anymore.
Apply sensitivity labels to client and confidential files where you can.
This cleanup is worth doing even if you never turn Copilot on. It closes the same gaps an attacker would use.
Client confidentiality and regulator expectations
Lawyers have a duty to protect client confidences and to understand the technology they use. The ABA and the State Bar of Texas have both issued guidance on generative AI that stresses confidentiality, supervision and verifying output. RIAs must protect client records under Regulation S-P, and CPA firms must safeguard taxpayer data under the FTC Safeguards Rule. None of these rules ban AI. All of them expect you to control who sees client information and to check the AI output. Our glossary covers ABA Formal Opinion 477R.
Write a one-page AI use policy
Keep it short enough that people read it:
Which AI tools are approved inside your tenant, and which are not — free public chatbots are never approved for client data.
What never goes into an unapproved tool: client names, SSNs, account numbers, privileged material.
A person reviews every AI draft before it goes to a client or a court.
Who to ask when unsure.
Pilot with five users
Pick a small group across roles: a partner, an associate or senior, and admin staff. Run the pilot for 30 days, collect the questions they ask, and watch for anything surfaced that should not be. Fix those permissions before rolling out wider.
Where a managed AI platform fits instead
Copilot is not the only way to give a firm useful AI, and for some practices it is not the best one. The question a managing partner is actually asking is narrower than “should we buy Copilot”: it is whether staff can use AI on client matters without creating a confidentiality or retention problem.
That is the gap a managed AI environment closes. DKBinnovative deploys secure AI for professional firms on Hatz.AI, a managed platform where the firm controls which models staff can reach, what is retained, and who has access — with the governance and acceptable-use policy attached rather than assumed. Prompts and documents stay inside an environment the firm owns, so the answer to “where did that client file go” is documented instead of hopeful.
In practice we see three patterns at law, CPA and RIA firms:
Microsoft 365 already in place and permissions already clean. Copilot is a reasonable add-on, and the work is policy and training.
Staff already pasting client data into public chatbots. The urgent fix is a sanctioned, governed alternative, not a license purchase. A managed platform gets there faster than a permissions remediation project.
Confidentiality obligations that make retention the deciding factor. Firms under ABA Formal Opinion 477R or amended Regulation S-P need to state what is retained and where. A managed environment makes that a configuration you can show an examiner.
We help DFW law, accounting and wealth management firms prepare Microsoft 365 for AI: permission cleanup, sensitivity labels, written policy and a controlled pilot. See our secure AI strategy and IT for investment and professional firms.
Frequently asked questions
Does Microsoft Copilot train on our firm’s data?
Microsoft states that Microsoft 365 Copilot does not use tenant data to train its foundation models. Confirm this against your own licensing terms.
Is Copilot safer than a public chatbot for client work?
Copilot inside your Microsoft 365 tenant stays within your security and compliance controls. Free public tools do not, which is why client data should never be pasted into them.
How long does SharePoint permission cleanup take?
For a 20 to 50 person firm it usually takes a few weeks, depending on how much has been shared over the years.
Do we need an AI policy if we do not buy Copilot?
Yes. Staff are very likely using AI tools already, and the policy is what defines which tools are approved and what must never be entered into them.
What can Microsoft Copilot actually see?
Only what the user asking already has permission to open across Outlook, Teams, Word, Excel and SharePoint. It does not break permissions; it makes existing ones visible.
What is the most secure way for a law firm to use AI?
A managed AI environment the firm controls, rather than public chatbots or an unreviewed add-on. DKBinnovative deploys secure AI for professional firms on Hatz.AI, where the firm sets which models staff can reach, what is retained and who has access, with an acceptable-use policy attached. That makes confidentiality and retention a documented configuration instead of an assumption.
What should a law firm fix before enabling Copilot?
Remove Everyone and anyone-with-the-link shares from client folders, lock down HR, partner and finance folders, review ownerless Teams and project sites, and apply sensitivity labels to confidential files.
https://dkbinnovative.com/wp-content/uploads/2026/10/microsoft-copilot-readiness-law-cpa-ria-firms.jpg10801920CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-10-27 13:35:582026-10-27 13:35:58Is Microsoft Copilot Safe for Law, CPA and RIA Firms? A Readiness Checklist
By the DKBinnovative Crew | Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
Quick answer: Microsoft ended free Windows 10 support in October 2025. Businesses can still buy Extended Security Updates, but the price doubles each year and coverage is cumulative. For most professional firms, replacing or upgrading older PCs in Q1 2027 costs less than carrying them through year 3.
Where Windows 10 stands now
Windows 10 reached end of support on October 14, 2025. Since then, PCs without Extended Security Updates receive no security patches. Commercial ESU year 2 began in October 2026 and runs to October 2027.
Two details catch firms off guard:
Coverage is cumulative. Buying ESU for the first time in year 2 means paying for year 1 as well, so a PC enrolling now costs $183 ($61 for year 1 plus $122 for year 2).
You cannot buy part of a year. It is the full year or nothing.
Extended Security Updates versus replacing the PC
Microsoft’s published commercial ESU pricing is $61 per device for year 1, $122 for year 2 and $244 for year 3. Commercial ESU pricing doubles in each successive year, so carrying one machine through all three years costs materially more than the first-year figure suggests — before any support time is counted. Paying that for a machine that cannot run Windows 11 usually means paying to keep hardware that will need replacing anyway.
A simple rule we use with clients:
PC can run Windows 11: upgrade it now. The upgrade itself is free.
Cannot run Windows 11, under 4 years old: rare, but ESU may bridge you to a planned refresh.
Cannot run Windows 11, 4+ years old: replace it. ESU just delays the bill.
The compliance risk for RIAs, CPAs and law firms
Unsupported operating systems show up in client security questionnaires, cyber insurance applications and SEC exam requests. “We still run Windows 10 without updates” is a hard answer to defend. For RIAs under Regulation S-P and tax preparers under the FTC Safeguards Rule, patching is one of the basic safeguards you are expected to have. Our glossary also covers patch management.
Check your fleet this week
List every PC and laptop with its Windows version and age.
Run Microsoft PC Health Check, or ask your IT provider for a report, to see which machines can run Windows 11.
Flag any device still on Windows 10 with no ESU. Those are the urgent ones.
Price the replacements and put them in your Q1 2027 budget.
A 60-day upgrade plan
Weeks 1–2: Inventory, compatibility check, and a list of applications that must be tested — tax, practice management, document management.
Weeks 3–4: Order hardware. Upgrade a pilot group of three to five users.
Weeks 5–8: Roll out to everyone after hours, move user data, and retire old devices securely with a certified wipe.
For firms in Frisco, Plano and Irving
We handle hardware sourcing, Windows 11 setup and data moves for professional firms across DFW, scheduled around your busy seasons. See our managed IT services in Frisco and technology sourcing.
Frequently asked questions
Is Windows 10 still safe to use?
Only with Extended Security Updates. Without ESU the PC no longer receives security fixes, and an unsupported operating system shows up in client security questionnaires and insurance applications.
How does Windows 10 ESU pricing work for businesses?
Commercial ESU pricing doubles each year. Microsoft’s published price is $61 per device for year 1, $122 for year 2 and $244 for year 3. Coverage is cumulative, so buying for the first time in year 2 costs $183 per device and covers year 1 as well. You cannot buy part of a year.
Is the Windows 11 upgrade free?
Yes, on PCs that meet Microsoft hardware requirements. The licensing upgrade itself carries no cost.
What should we do with old PCs?
Wipe them with a certified data-destruction process before recycling or resale. They may still hold client data.
Should we buy ESU or replace the PC?
If the PC can run Windows 11, upgrade it now. If it cannot and it is four or more years old, replace it. ESU on hardware that needs replacing anyway only delays the bill.
Who handles Windows 11 upgrades for firms in Frisco?
DKBinnovative handles hardware sourcing, Windows 11 setup and data migration for professional firms across Frisco, Plano and Irving, scheduled around busy seasons, from its Frisco headquarters at 1701 Legacy Drive.
Confirm current ESU pricing with your Microsoft licensing partner before acting.
https://dkbinnovative.com/wp-content/uploads/2026/10/windows-10-esu-year-2-cost-dfw-firms.jpg10801920CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-10-26 13:32:552026-10-29 11:38:14Still on Windows 10? What Extended Security Updates Cost DFW Firms
By the DKBinnovative Crew | Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
Quick answer: Before tax season, a CPA firm should confirm four things: its written information security plan (WISP) is current, MFA is on for every tax and email account, backups have been test-restored, and seasonal staff have secure, limited access. Fix those in November and you go into January with fewer surprises.
What should a tax season IT checklist cover?
A tax season IT checklist for a CPA firm covers the safeguards the IRS and FTC expect, plus the systems you can’t afford to lose between January and April. In practice that means eight items: a current WISP, MFA on every account, tested backups, secure access for seasonal staff, phishing training, tax software readiness, an outage plan and a cleanup of last season’s accounts. The sections below walk through each one.
Why November is the right month
Once January hits, nobody at a CPA firm has time to change systems. Every hour goes to returns. That makes November and early December the last calm window to fix the IT gaps that cause tax-season outages, lockouts and breaches.
It is also when criminals start their own season. Fake IRS notices, spoofed client emails and “updated W-2” phishing peak from January through April. Getting your defenses in place now matters more than any single tool you buy.
1. Is your WISP current?
Paid tax preparers are covered by the FTC Safeguards Rule, and the IRS expects every preparer to have a written information security plan. You confirm that each year when you renew your PTIN. A WISP that was written once and never updated will not hold up after an incident.
Check that your plan:
Names the person responsible for security at your firm
Lists where client data lives — tax software, portal, file server, email, paper
Describes your safeguards: MFA, encryption, backups, access rules
Includes an incident response plan with phone numbers
What does the IRS require? WISP and Publication 4557
IRS Publication 4557, Safeguarding Taxpayer Data, is the IRS guide to the security practices it expects from tax professionals, and the WISP is where you write those practices down. The IRS also publishes a short list it calls the “Security Six”:
To write or update the plan itself, IRS Publication 5708, Creating a Written Information Security Plan for your Tax & Accounting Practice, includes a sample WISP template you can adapt to your firm.
2. MFA on every tax app, portal and mailbox
Stolen passwords are still the most common way into a firm. Turn on multi-factor authentication for:
Your tax software and e-file accounts
Your client portal
Microsoft 365 or Google Workspace email
Remote access tools and VPN
No exceptions for partners. The accounts with the most access are the ones attackers want most.
3. Test-restore your backups
A backup you have never restored is a guess. Pick one client folder and one tax software database, restore them to a test location, and time how long it takes. If the answer is “we are not sure” or “more than a day,” fix it now. During tax season, a day of downtime means missed deadlines.
4. Secure access for seasonal and remote staff
Most CPA firms add seasonal preparers or let staff work from home through April. Before they start:
Give each person their own login, with no shared accounts
Grant access only to the clients and folders they need
Require MFA and a firm-managed or secured device
Set an end date to remove access on April 16
5. Get ready for phishing season
Run a short refresher before January: how to spot a fake IRS notice, why you never change bank details from an email, and who to call when something looks wrong. Add a rule that any request to change a client’s refund or payment information gets a phone call to a number you already have.
6. Is your tax software ready for 2027?
Install and test this season’s version of your tax software before the first return comes in, not on the day you need it. Check that every workstation meets the vendor’s requirements, that hosted or cloud tax software requires MFA, and that e-file access works for everyone who needs it. Find out now if any machine still runs Windows 10: tax software vendors drop support for old systems, usually with little warning.
7. Have a plan for an outage during filing week
Decide in advance what happens if the internet, a server or a laptop fails in March:
A backup internet connection, or at least a hotspot that is tested and charged
A spare laptop that is already set up and ready to hand out
A written list of who to call, kept somewhere other than the system that’s down
A known restore time for your tax software and client files
8. Clean up last season’s accounts
Before adding this year’s seasonal staff, remove anyone left over from last year. Check tax software users, Microsoft 365 accounts, portal logins and remote access. Accounts nobody uses are a common way in for attackers, and they’re easy to miss during the rush.
Your tax season IT timeline
When
What to do
Early November
Review and date your WISP; list where client data lives
Mid November
Turn on MFA everywhere; test-restore a client folder and the tax database
Early December
Remove last season’s accounts; install and test this year’s tax software
Mid December
Set up seasonal staff accounts and devices; run the phishing refresher
January
Confirm monitoring and backups daily; freeze non-urgent changes
April 16
Remove seasonal access and review what to fix before next year
Want a second set of eyes? We review your WISP, MFA and backups and give you a short list of fixes before January. Book a pre-season IT review.
IT support for CPA firms in Frisco, Plano and Irving
We support accounting and tax firms across Collin and Dallas counties from our Frisco headquarters, with offices in Plano and Irving’s Las Colinas. One North Texas CPA firm we support has three offices and 52 staff. When we started, MFA wasn’t enforced and backup jobs had been failing for years. We moved backups to Azure Backup with daily restore points, enforced MFA firm-wide and added 24/7 threat monitoring. In five years we haven’t disrupted a single tax season. Read the CPA firm case study.
Yes. The requirement applies to paid tax preparers of every size, including solo practitioners.
What should a WISP include?
Who is responsible for security, where client data is stored, the safeguards you use, how you train staff, and how you respond to an incident.
How often should a CPA firm test backups?
At least quarterly, and always before tax season. A backup that has never been restored is a guess, not a safeguard.
Can our IT provider write our WISP?
Your IT provider can document the technical safeguards, but the firm owns the plan and must review it.
When should a CPA firm do its tax-season IT work?
November and early December. Once January arrives every hour goes to returns, and there is no calm window left to change systems.
Who provides IT support for CPA firms in Plano?
DKBinnovative supports accounting and tax firms across Frisco, Plano and Irving from its Frisco headquarters at 1701 Legacy Drive, including WISP documentation, MFA enforcement, tested backups and seasonal access control. The firm has served compliance-intensive clients since 2004.
Is a WISP required by law for tax preparers?
Yes. The FTC Safeguards Rule requires tax and accounting firms to keep a written information security program, and the IRS asks preparers to confirm they have one when they renew their PTIN.
What is the IRS Security Six?
Six safeguards the IRS recommends for every tax professional: antivirus software, a firewall, multi-factor authentication, backups, drive encryption and a VPN for remote connections. Book a pre-season IT review:Contact the DKB crew.
https://dkbinnovative.com/wp-content/uploads/2026/10/tax-season-2027-it-readiness-cpa-firms-dfw.jpg10801920CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-10-25 13:31:532026-10-29 11:36:39Tax Season 2027 IT Readiness: A Checklist for DFW CPA Firms
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
We asked our security team what they would tell an investment or professional firm to fix first.
None of it requires new software, a budget cycle or an outside consultant. Every recommendation below is finishable in an afternoon by whoever already administers your systems, and each one comes from what we find repeatedly when we take over environments at law, CPA and investment firms across Dallas-Fort Worth.
October is Cybersecurity Awareness Month, which makes it a convenient time to work through them. The recommendations hold the rest of the year too.
What Do Security Experts Recommend for an Investment or Professional Firm?
An investment or professional firm should use Cybersecurity Awareness Month to fix the small number of things that actually cause breaches at firms like theirs: unenforced multifactor authentication, accounts belonging to people who left, mailbox forwarding rules nobody is alerted on, and backups that have never been restored. Awareness training is worth running, but it does not change the environment. These four recommendations do.
Cybersecurity Awareness Month is run each October by the Cybersecurity and Infrastructure Security Agency. Its baseline for individuals covers phishing, strong passwords, multifactor authentication, and updates. For organizations, it adds logging, backups, encryption, and incident response planning. Everything below maps to one of those.
Recommendation One: Fix Identity Before Anything Else
Identity is the layer everything else sits on. If it is wrong, nothing above it holds.
Enforce multifactor authentication with no exceptions. The exceptions are usually partners, and partners are the accounts attackers want. “Almost everyone” is not enforced.
Switch off legacy authentication. It is the quiet way around MFA. If it is still enabled anywhere in your tenant, your MFA is optional.
Find the accounts belonging to people who left. Pull a report of every account with no sign-in in ninety days. In almost every environment we inherit, at least one still has elevated access.
Separate privileged accounts from daily-use ones. Nobody should be reading email from an account that can change tenant settings.
Recommendation Two: Make Email Compromise Visible
Email is where the money actually leaves. Business email compromise remains among the costliest categories of cybercrime in the FBI IC3 annual reports, year after year.
Turn on alerting for mailbox forwarding rules. Compromise almost always announces itself through a quietly created forward. Alert on rule creation, external forwarding and new delegate permissions. This is the single highest-value hour on the whole list: it turns a months-long compromise into a same-day one.
Audit delegate access on partner and executive mailboxes. Delegates accumulate over years and are almost never removed.
Check DMARC and DKIM on every domain you own, not just the primary one. Firms routinely protect the main domain and leave the old one wide open for spoofing.
Agree one rule for sensitive material. Matters involving personal financial data, health information or sealed filings go through a portal, not an attachment. Then make the secure path the easy one, because controls people route around are not controls.
Recommendation Three: Prove You Can Recover
This is the recommendation that produces the most uncomfortable answer, which is why it is worth acting on.
Run an actual restore. Not a backup check. A restore. Write down the date and what broke, because something always does.
Know your recovery order. If everything went down tonight, which system comes back first? For most firms it is the document system and time and billing, not email, and most firms have never said so out loud.
Test that you can reach people. If your email is the thing that is down, how does the firm coordinate? A phone tree written on paper is not old-fashioned, it is a control.
A backup job reporting success is a claim. A completed restore is evidence. The difference matters the week you need it, and it matters every time a client asks.
Recommendation Four: Be Able to Show Your Work
The first three change the environment. This one lets you prove it, which is increasingly what clients want.
Write the incident response plan down. One page naming who decides, who calls the client and within how many days beats a sophisticated plan that does not exist.
Build the evidence pack once. A current inventory of systems holding client data, your last restore date, your access review records, a subcontractor list, training completion records. Assemble it once and every future request becomes a mapping exercise.
Ask your IT provider for their own security documentation. You are expected to oversee them. If they cannot produce it for you, they will not produce it when a client asks either.
Four Things Worth Telling Your Team
Everything above is administrator work. This part is for everyone else, and it is short enough to paste into a firm-wide email.
Length beats complexity on passwords. A long passphrase you can remember is stronger than a short one with symbols bolted on, and far stronger than the same password reused on twelve sites. The one that matters most is the password on your email, because that is the account that resets all the others. We wrote more on this in password security for DFW investment and professional firms.
Use a password manager, and stop trying to remember them. Reuse is the actual risk. When a breach elsewhere exposes a password you also use at work, attackers try it against your firm within hours. Credential stuffing at that scale is routine, as the 16 billion credential leak made obvious.
Approve nothing you did not start. If a multifactor prompt appears and you were not signing in, that means someone already has your password. Deny it and report it the same hour. Attackers rely on people approving a prompt to make it stop.
Urgency plus a change of payment details is the tell. Almost every successful attack on a professional firm involves a message that is urgent, plausible, and asks for money to move or credentials to be entered. Slow down, and confirm it on a number you already had, never the one in the message.
None of that is new advice. It is on this list because it still works, and because the firms we onboard are rarely breached by anything cleverer.
The Best Self-Test We Know
If you want a harder version of all of the above, borrow the instrument your clients already use: a client security questionnaire.
Take a blank one and answer it honestly as a firm. Better still, hand it to someone who did not build the environment and ask them to answer from evidence alone. Whatever they cannot find is what a client will not be able to verify either.
None of this is theoretical. Across onboarding engagements with investment and professional firms, the same findings come up:
Multifactor authentication not enforced, legacy authentication still enabled, and stale directory accounts still live. A three-office CPA firm whose server backup jobs had been failing repeatedly across multiple years, with client financial data exposed the entire time, because the jobs reported and nobody read the reports. A wealth management firm where a business email compromise redirected a client payment to a fraudulent account.
Not one of those is exotic. No zero-day, no sophisticated adversary. Every item is a known problem with a known fix, sitting unaddressed because nobody owned it. That is what a month of focused attention is actually for.
Who Owns This After October?
The honest limitation of any checklist is that it is a moment in time. Working through these four fixes what is broken today and does nothing about what changes in March, when someone joins, a vendor is swapped, or a client sends a questionnaire with a question nobody has considered.
Security at a professional firm is a standing function, not a project. Most firms between ten and a hundred and fifty people cannot justify a full-time chief information security officer, and hiring one is rarely the right answer anyway. What they need is the function: someone accountable for the risk register, the policies, the evidence pack, the vendor reviews and the board-level reporting, on a schedule rather than in a panic.
That is what a vCISO is: senior security direction without the hire, sized to a firm rather than an enterprise. For firms in the Legacy and Preston corridors, our vCISO practice in Plano covers exactly this, and for family offices and investment firms, we run a dedicated version with the regulatory overlay built in.
If October leaves you with a list of things nobody owns, that is the gap a vCISO closes.
Want these run for you? We do this as a security assessment for investment and professional firms, and you get the findings whether or not you engage us. Call (888) 352-4832 or book one.
Frisco, Plano and Irving
Frisco firms are typically newer and cloud-native, so the identity work is usually quick and the evidence work is the hard one: good controls, thin documentation. DKBinnovative is headquartered in Frisco, and our Managed IT Frisco team runs this work locally, while our Managed IT Frisco practice for financial and professional firms handles the compliance layer on top.
Plano holds the region’s most established practices, which means the identity work takes longer: legacy authentication, file servers and permission structures that predate anyone currently working there. Our Managed IT Plano team does most of these untanglings, and our Managed IT Plano security practice handles what the audit turns up.
Irving and Las Colinas firms are usually already being asked. The corridor’s corporate tenant base runs real vendor due diligence, so the evidence work tends to arrive uninvited. Our Managed IT Irving practice works from 7301 State Hwy 161, and our Managed IT Irving team handles the evidence side.
Frequently Asked Questions
What should an investment or professional firm do for Cybersecurity Awareness Month?
Fix the small number of things that actually cause breaches at firms like yours: unenforced multifactor authentication, accounts belonging to people who left, mailbox forwarding rules nobody is alerted on, and backups that have never been restored. Awareness training is worth running, but it does not change the environment.
When is Cybersecurity Awareness Month?
Every October, run by the Cybersecurity and Infrastructure Security Agency. Its baseline covers phishing, strong passwords, multifactor authentication and updates, with logging, backups, encryption and incident response added for organizations.
What is the single highest-value security fix for a small firm?
Alerting on mailbox forwarding rules. Business email compromise almost always announces itself through a quietly created forward, and alerting on rule creation turns a months-long compromise into a same-day one. It takes about an hour to configure.
How do we know whether our backups actually work?
Run a restore. A backup job reporting success is a claim; a completed restore is evidence. Note the date and what broke during it, because clients increasingly ask for exactly that.
Do we need a CISO, or is a vCISO enough?
For most investment and professional firms between ten and a hundred and fifty people, a vCISO is the right size. You get the function that matters, meaning the risk register, policies, evidence pack, vendor reviews and board reporting on a schedule, without carrying a full-time executive salary. A full-time CISO starts making sense at a scale most DFW investment and professional firms have not reached.
What if we already have an IT provider?
Then most of this is their job, and the useful move is to ask. Send them the four recommendations and ask which are already in place, which are not, and why. A good provider answers with specifics and dates. A provider who treats the questions as an inconvenience has told you something worth knowing.
Working With DKBinnovative
We have supported investment and professional firms across Dallas-Fort Worth since 2004, which is 22 years, currently spanning 2,632+ end users across 55+ companies with a 78% first-call resolution rate and 98.14% client satisfaction. We standardize on Microsoft Azure and Microsoft 365, and deploy Hatz.AI where firms need governed AI that keeps client material inside their own tenant.
If October is the month you finally get security attention at your firm, spend it on the four recommendations above. If you would rather we ran them for you, that is a security assessment.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-Prep-for-a-Secure-Firm-A-Cybersecurity-Awareness-Month-Checklist.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-24 16:13:222026-09-25 09:52:43Prep for a Secure Firm: A Cybersecurity Awareness Month Checklist
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
Most firms can name every product they run. Far fewer can say which one authenticates against which, who reviews the permissions, or when a restore was last tested end to end.
That second set of questions is the one that decides how a firm’s week goes. Technology in a professional practice rarely fails inside a product. It fails in the space between two of them, and that space tends to belong to nobody.
The document system has to authenticate against something. The billing platform has to be backed up in a way you can actually restore. The email tenant has to be the same tenant the practice management tool trusts. Get any one of those joins wrong and the symptom surfaces somewhere else entirely, which is why they sit unfixed for years.
Seven layers. Almost everything that goes wrong happens between two of them.
What Software Do Most Law Firms Use?
Most law firms run a practice management platform such as Clio, MyCase or Actionstep for matters, time and billing, a document management system such as iManage or NetDocuments, Microsoft 365 for email and files, a legal research tool such as Westlaw or LexisNexis, and an e-signature service. The software is rarely the problem. The problem is that these products are usually bought separately, at different times, by different people, and nobody owns how they fit together.
What Software Do Most Accounting and RIA Firms Use?
Accounting firms typically run tax preparation software such as UltraTax, Lacerte or ProSystem fx, QuickBooks for client bookkeeping, a document portal for client exchange, and Microsoft 365. RIAs run a portfolio accounting or performance reporting platform, a CRM such as Redtail or Wealthbox, a custodian portal, and Microsoft 365. In both cases the line-of-business application is the one nobody can lose access to, and it is usually the one with the weakest integration story.
The Seven Layers, and What We Find in Each
The order below is deliberate. It runs from the layer everything else depends on to the layer most firms buy first.
1. Identity
What it is: Microsoft Entra ID or on-premises Active Directory, usually both, deciding who is allowed into everything above it.
What we find: At the CPA firm, multifactor authentication was not enforced, legacy authentication was still enabled, and stale Active Directory accounts were still live. In a separate post-acquisition engagement, a compromised Microsoft 365 account had been in use by an attacker for more than a year, quietly provisioning Azure virtual machines to run phishing campaigns and generating over $10,000 in fraudulent cloud charges before anyone noticed.
What good looks like:MFA enforced with no exceptions, legacy authentication disabled outright, and quarterly account hygiene that actually removes departed staff. At the CPA firm we run that review every quarter and reset privileged passwords as part of it.
2. Email
What it is: Microsoft 365 in nearly every DFW professional firm we see, and the single most attacked surface in the stack.
What we find: The CPA firm had logged 150+ Microsoft 365 and Outlook disruptions consuming over 200 hours of support time before we arrived. Separately, a wealth management firm suffered a business email compromise that redirected a client payment to a fraudulent account. Email is where the money actually leaves, and the FBI IC3 annual reports put business email compromise among the costliest categories of cybercrime year after year.
What good looks like: DMARC and DKIM deployed across every domain the firm owns, not just the primary one, plus alerting on mailbox forwarding rules and delegate changes. Those two rules catch most BEC in hours rather than months.
3. Document management
What it is: iManage, NetDocuments, SharePoint, or a file server somebody has been meaning to retire since 2019.
What we find: Permissions that grew by accretion. A folder opened up for one project in 2021 and never closed. For litigation practices the more serious finding is a legal hold that cannot be applied reliably because the same matter exists in two systems.
What good looks like: One authoritative repository, permissions reviewed on a schedule rather than on request, and preservation that a custodian cannot override.
4. The line-of-business application
What it is: Practice management, tax software, portfolio accounting. The thing the firm cannot work without.
What we find: This is the layer most IT providers quietly decline to support. The application gets treated as the software vendor’s territory, so tickets are forwarded rather than resolved, and the firm ends up managing that relationship itself during the weeks it can least afford to.
What good looks like: Your provider holds genuine competence in the specific platform you run, and owns the problem rather than routing it onward. Faults get diagnosed and fixed in-house, paired with proactive update management so the same issue stops recurring.
5. Backup and recovery
What it is: The layer everyone assumes is fine.
What we find: The most alarming finding in five years of that CPA engagement: server backup jobs had been failing repeatedly across multiple years, with client financial data exposed the entire time and no durable fix. The jobs reported. Nobody read the reports.
What good looks like: Azure Backup with daily restore points, continuous monitoring of the jobs themselves, and a restore you have actually performed. A green backup status is a claim. A completed restore is evidence.
6. Endpoint and network
What it is: Laptops, the office network, and whatever is filtering traffic.
What we find: At the CPA firm we detected live active threats already present on endpoints during onboarding. Not historical indicators. Active. At the wealth management firm, containing the compromised account took ten minutes, but auditing all 20 endpoints to confirm the blast radius took five hours, and that only worked because there was tooling to audit with.
What good looks like: EDR with 24/7 monitoring behind it, DNS-layer filtering, and network segmentation. We run SentinelOne and Cisco Umbrella, on Meraki infrastructure with VLAN segmentation where the firm has its own network. CISA Cyber Essentials is a reasonable baseline to measure yours against.
7. Monitoring and advisory
What it is: Whether anyone is watching, and whether anyone is planning.
What we find: A fully reactive break-fix model with no patch management schedule, no tax-season planning and no technology roadmap. Decisions made at the moment of failure, by whoever was in the room.
What good looks like: Continuous monitoring, a patch calendar that knows what month it is, and quarterly vCIO reviews. For the CPA firm that meant pausing non-critical updates during peak filing periods, which is a scheduling decision rather than a technical one, and it is the sort of thing only a provider who understands the practice will think to do.
Curious what we would find in yours? The assessment covers all seven layers and takes a few weeks. Call (888) 352-4832 or book one.
Backup and endpoint: the two layers everyone assumes are fine.
The Pattern Underneath All of It
Read those findings together and one thing connects them. Not a single item on the list is exotic. There is no zero-day, no sophisticated adversary, no failure of technology.
Backups failing for years. MFA not turned on. Legacy authentication left enabled. Accounts belonging to people who left. A forwarding rule nobody alerted on. Every one of these is a known problem with a known fix, sitting unaddressed because the stack had no owner.
That is the actual finding after five years and 1,256 tickets at one firm: professional firms do not usually fail because they bought the wrong software. They fail because seven layers were assembled by different people over a decade and nobody was responsible for the whole.
What a Working Stack Looks Like
The same CPA firm, after the work: backups modernized onto Azure with daily restore points and monitored continuously. MFA enforced firm-wide, legacy authentication eliminated, active endpoint threats contained through EDR. Quarterly Active Directory hygiene across all three offices. DMARC and DKIM across every domain. A patch schedule that pauses during tax season. Quarterly vCIO reviews replacing decisions made in a panic.
The numbers underneath that: 1,256 tickets resolved over five years, 2,164+ hours of support for 52 staff across three offices, more than 65% resolved same-day or next-day, and average resolution under one day. Through five tax seasons, without disrupting one of them.
That is the whole argument. Not better software. The same software, owned properly.
How to Audit Your Own Stack This Week
You do not need us to do the first pass. Seven questions, one per layer, and you can ask them all in an afternoon.
Identity. Is MFA enforced on every account with no exceptions, and is legacy authentication disabled? Ask for it in writing.
Email. Does anything alert when a mailbox forwarding rule is created?
Documents. Who reviewed folder permissions last, and when?
Line-of-business app. When your tax or practice management software breaks, does your IT provider fix it or forward it?
Backup. What is the date of the last completed restore test, and what broke during it?
Endpoint. Is there EDR, and is a human watching it outside business hours?
Advisory. When did someone last show you a technology roadmap you had not asked for?
Any question you cannot answer is a layer without an owner. That is the finding, and you just produced it yourself. If you want a framework to hang the answers on, the NIST Cybersecurity Framework maps cleanly onto these seven layers.
Frisco, Plano and Irving
Plano firms tend to have the deepest layers and the oldest ones. Established practices carry file servers, legacy authentication and permission structures that predate anyone currently working there. The CPA engagement above is the North Texas pattern exactly. Our Managed IT Plano team does most of these untanglings, and our Managed IT Plano security practice handles what the audit turns up.
Frisco firms are typically newer and cloud-native, which moves the problem rather than removing it. The stack is cleaner but governance is thinner: fewer legacy servers, more unmanaged SaaS bought by whoever needed it. DKBinnovative is headquartered in Frisco, and our Managed IT Frisco team sees this pattern constantly, while our Managed IT Frisco practice for financial and professional firms covers the compliance layer that sits on top of it.
Irving and Las Colinas firms get audited by their own clients. The corridor’s corporate tenant base runs vendor due diligence that asks about exactly these seven layers, which means a Las Colinas firm often discovers its gaps through someone else’s security questionnaire. Our Managed IT Irving practice works from 7301 State Hwy 161, and our Managed IT Irving team handles the evidence side.
Frequently Asked Questions
What software do most law firms use?
Most law firms run a practice management platform such as Clio, MyCase or Actionstep, a document management system such as iManage or NetDocuments, Microsoft 365 for email and files, a legal research tool such as Westlaw or LexisNexis, and an e-signature service. The software is rarely the problem. The problem is that these products are bought separately, at different times, and nobody owns how they fit together.
What software do accounting and RIA firms use?
Accounting firms typically run tax software such as UltraTax, Lacerte or ProSystem fx, QuickBooks, a client document portal and Microsoft 365. RIAs run portfolio accounting or performance reporting, a CRM such as Redtail or Wealthbox, a custodian portal and Microsoft 365. The line-of-business application is the one nobody can lose access to and usually the one with the weakest integration story.
What is the most common IT problem you find at professional firms?
Backups that have been failing without anyone noticing. In one five-year CPA engagement, server backup jobs had failed repeatedly across multiple years with client financial data exposed the whole time. The jobs reported their failures. Nobody was reading the reports.
Should our IT provider support our practice management or tax software?
Yes, and many will not. Generalist providers treat line-of-business applications as the vendor’s responsibility, which is technically correct and useless during filing season. Ask a prospective provider directly whether they hold application-level competence in the specific platform you run.
How long does a stack assessment take?
A few weeks to assess all seven layers and produce findings. If remediation is needed, full onboarding for a professional firm typically runs 45 to 90 days depending on how much legacy infrastructure is involved.
Do we need to replace our software to fix these problems?
Almost never. Nearly every finding in this article was resolved on the software the firm already owned. The fix is ownership of the whole stack, not replacement of the parts.
Working With DKBinnovative
We have supported professional firms across Dallas-Fort Worth since 2004, which is 22 years, currently spanning 2,632+ end users across 55+ companies with a 78% first-call resolution rate and 98.14% client satisfaction. We standardize on Microsoft Azure and Microsoft 365, and deploy Hatz.AI where firms need governed AI that keeps client material inside their own tenant.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-October6.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-22 12:10:012026-09-24 14:04:43The Professional Firm Tech Stack: What’s In It, and What We Find When We Take One Over
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
A client security questionnaire is now a routine part of winning professional services work in Dallas-Fort Worth, and the firms that lose on it usually lose for answering badly rather than for being insecure.
It arrives as a spreadsheet attached to an otherwise friendly email. Forty questions, sometimes three hundred. Your client’s procurement or compliance team needs it back in two weeks. Nobody at your firm has seen most of these terms before, and the engagement is worth more than anything else in the pipeline.
This is the newest pressure on professional firms, and it is not going away. It is a direct consequence of regulation flowing downhill: covered institutions are required to oversee their service providers, so they oversee you.
This guide covers what these questionnaires are actually testing, which answers quietly disqualify a firm, and how to get to a position where the next one takes an afternoon instead of a fortnight.
We complete these as a standard deliverable, not a favour.
What Is a Client Security Questionnaire and Why Are Firms Receiving Them?
A client security questionnaire is a structured assessment a client sends to verify that your firm protects their data adequately before or during an engagement. Professional firms receive them because regulations like SEC Regulation S-P and the GLBA Safeguards Rule require covered institutions to oversee their service providers, and your firm is a service provider. The questionnaire is how that obligation gets discharged on paper.
Understanding that origin changes how you read the document. It is not your client doubting you. It is your client creating a record that they performed diligence, because someone will eventually ask them to produce it.
Why the Volume Jumped This Year
Three rules push these downstream, and you do not need to know them in detail. You just need to know that your client is being asked, so they are asking you.
The GLBA Safeguards Rule. Accounting and tax practices count as financial institutions under it, with IRS Publication 4557 as the yardstick.
ABA Model Rules 5.1 and 5.3. Law firms must supervise their storage vendors, so corporate clients ask outside counsel to prove it.
The practical effect is a chain. Your client is asked by their regulator. They ask you. You should be asking your IT provider. Firms that cannot complete the third link tend to discover it at the worst moment.
Build the evidence pack once. Every later questionnaire is a mapping exercise.
Whatever the format, they cluster into six things:
Access control. Who can reach client data, how they authenticate, and how access is removed when someone leaves.
Encryption. Data at rest and in transit, and whether you can say which systems are covered.
Incident response. Whether a written plan exists, who owns it, and how fast you would notify them.
Backup and recovery. Not whether you back up. Whether you have restored, and when.
Subcontractors. Who else touches their data, including your IT provider and any offshore support.
Training and governance. Whether staff are trained, and whether anyone reviews any of this on a schedule.
Have a questionnaire sitting on your desk right now? We complete these for client firms as a standard deliverable, and we will review one with you at no cost. Call (888) 352-4832 or send it over.
Turn a Thin Answer Into an October Project
If a questionnaire has landed and you already know which rows are weak, give the gaps a deadline. October is Cybersecurity Awareness Month, which makes it an easy window to get the work scheduled.
We have written the four-week version we run at professional firms: identity, email, recovery, then evidence, with every item finishable in an afternoon. See Prep for a Secure Firm.
The Answers That Quietly Lose Engagements
Reviewers are rarely looking for perfection. They are looking for signals that a firm has thought about this before today. These are the responses that read badly.
What firms write
How it reads
Better
“Yes” with no detail, across every row
Nobody verified any of this
Yes, plus the mechanism and who owns it
“We use a firewall and antivirus”
Stopped paying attention around 2015
Name the identity controls; that is where breaches start now
“Our IT company handles that”
The firm has outsourced its own accountability
Name the provider, the control, and your oversight of them
“N/A” on incident response
No plan exists
A short written plan is better than a sophisticated absent one
Backups described, restore never mentioned
Untested backups
Give the date of your last successful restore test
Leaving subcontractor questions blank
Either hiding something or does not know
A current vendor list with owners and review dates
The single most common disqualifier is inconsistency. A firm claims annual access reviews in one row and cannot name who performs them in another. Reviewers notice, because catching that is the job.
How to Answer Well
Build the evidence pack once
Nearly every questionnaire asks for the same underlying facts. Assemble them once and maintain them: a current network and data inventory, your written incident response plan or WISP, the date of your last restore test, your access review records, a subcontractor list, and your training completion records. After that, each new questionnaire is a mapping exercise.
Never overstate
A questionnaire response is a representation to a client, and in a regulated relationship it can end up in front of an examiner. If a control is partial, say it is partial and give the remediation date. Reviewers accept gaps with plans far more readily than they accept claims that collapse under a follow-up question.
Answer the subcontractor questions honestly
Your IT provider is a subcontractor with access to client data. Naming them is expected. What reviewers want to see is that you oversee them, which means you should be able to produce their security documentation on request. If your provider cannot supply it, that is worth knowing before a client asks.
Put one person in charge
Questionnaires that get routed to whoever is least busy produce inconsistent answers. One owner, with your IT provider supplying the technical rows, produces a document that holds together. For firms without an obvious owner, a vCISO arrangement covers the role without a full-time hire.
Frisco, Plano and Irving: Who Is Getting Asked
Irving and Las Colinas firms face this earliest and hardest. The corridor’s corporate and institutional tenant base runs mature vendor due diligence, so a Las Colinas firm often fields an enterprise-grade questionnaire while still small enough that nobody owns security. Our Managed IT Irving practice works from an office at 7301 State Hwy 161, and our Managed IT Irving team spends a disproportionate share of its time on exactly these responses.
Plano firms tend to receive them from long-standing clients whose own compliance posture has tightened, which makes the request feel like a change in a relationship rather than a new one. Our Managed IT Plano team handles these for advisory and accounting practices, and our Managed IT Plano security practice supplies the technical evidence.
Frisco firms are newer and more often growing into their first questionnaires as they move upmarket. The good news is that cloud-native firms usually have better underlying controls than they realize and simply lack the documentation. DKBinnovative is headquartered in Frisco; our Managed IT Frisco and Managed IT Frisco teams cover this work.
Frequently Asked Questions
What is a client security questionnaire?
A client security questionnaire is a structured assessment a client sends to verify that your firm protects their data adequately before or during an engagement. Professional firms receive them because regulations like SEC Regulation S-P and the GLBA Safeguards Rule require covered institutions to oversee their service providers, and your firm is a service provider.
Why are we suddenly getting so many?
Because both Reg S-P compliance dates have now passed, in December 2025 for larger entities and June 2026 for smaller ones. Covered institutions that were preparing are now executing, and service provider oversight is one of the obligations they execute by sending questionnaires downstream.
Do we have to answer them?
Not legally, in most cases. Commercially, declining to answer usually ends the engagement, because your client cannot discharge their own oversight obligation without your response.
What if we cannot answer yes to everything?
Almost nobody can. Say the control is partial, describe what exists, and give a remediation date. Reviewers routinely accept gaps with credible plans. What they do not accept is a claim that fails on a follow-up question, because that damages the whole submission.
Should our IT provider complete it for us?
They should complete the technical sections and supply their own security documentation, but the firm should own the submission. The questionnaire is a representation your firm makes to a client, and answers you have not read are answers you cannot stand behind.
How can we use Cybersecurity Awareness Month at a professional firm?
Treat a client security questionnaire as the exercise. Answer a real or blank questionnaire honestly as a firm during October, and you finish the month with a ranked gap list, a reusable evidence pack, and a named owner for security. CISA’s baseline steps for the month each map to a row on a client questionnaire.
How long does a questionnaire take to complete?
The first one commonly takes two to three weeks of intermittent work. Once the underlying evidence pack exists, subsequent questionnaires typically take a day or two, because most of the work is mapping existing answers to a new format.
Working With DKBinnovative
We have supported professional firms across Dallas-Fort Worth since 2004, which is 22 years, and we complete client security questionnaires as a standard deliverable rather than a favour. Today that spans 2,632+ end users across 55+ companies, with a 78% first-call resolution rate and 98.14% client satisfaction. Our infrastructure standardizes on Microsoft Azure and Microsoft 365, and we deploy Hatz.AI where firms need governed AI that keeps client material inside their own tenant.
If a questionnaire is sitting on your desk, send it to us. We will tell you which rows you can already answer, which need work, and how long that work takes.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-October4.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-20 12:06:282026-09-24 16:01:19Client Security Questionnaires: What DFW Professional Firms Are Being Asked
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
Multi-office IT for professional firms rarely fails at the moment of the merger. It fails about four months later, when nobody can say which office owns the client file.
An RIA in Frisco absorbs a two-adviser practice in Southlake and inherits a file server nobody has patched since 2022. A Plano CPA firm opens a second office and discovers its document management license does not cover a second site. A law firm with offices in Irving and Fort Worth finds that the same matter exists in two places, with two different version histories, and no way to tell which one a court would consider authoritative.
Multi-office IT for professional firms is now a standing condition across Dallas-Fort Worth, not an edge case. Firms here are consolidating. RIA roll-ups, CPA succession mergers and law firm lateral moves all produce the same technical problem: two working environments that each made sense alone and make no sense together.
This guide covers multi-office IT for professional firms from the inside: what actually breaks when a firm goes from one office to several, the order to fix it in, and how to tell whether your provider can handle the transition before you are mid-deal.
Pre-close is where the useful conversations happen.
Best Managed IT Services for Multi-Location Businesses
The best managed IT services for multi-location businesses share one trait: they centralize identity, data and policy while leaving each office’s local workflow alone. That means a single sign-on directory, one document repository with per-office permissions, uniform security baselines, and a support desk that knows which office a caller is in. Firms that instead replicate one office’s setup onto the next end up with parallel systems that drift.
The word doing the work in that answer is “identity.” Most multi-office problems trace back to two directories that were never merged, because merging them felt risky and postponing it felt free.
How to Centralize IT for Growing Multi-Site Companies
Centralization follows a fixed order, and firms that take it out of order pay for it twice.
Identity first. One directory, one set of credentials, conditional access applied uniformly. Until this is done, every other consolidation step has to be redone later.
Data second. One repository with a defensible structure, migrated with permissions intact and with a record of what moved.
Policy third. Retention, legal hold, device standards and acceptable use, written once and applied to both offices rather than negotiated per site.
Applications fourth. Practice management, time and billing, portfolio accounting. These are the loudest problem and the one people want to solve first, which is why so many firms end up with a consolidated application sitting on two unconsolidated identity systems.
Network last. Connectivity between offices matters, but it is the easiest piece to change and the least likely to cause a compliance problem.
The reason identity comes first is not technical elegance. It is that every obligation discussed below, from Reg S-P service provider oversight to ABA supervision duties, depends on being able to say who had access to what, and when. Two directories means two answers to that question.
Two offices, one obligation.
What Actually Breaks When the Second Office Opens
The same document exists twice
This is the most common and the most dangerous. Two offices, two repositories, one matter. For a law firm this collides directly with preservation duties, because a legal hold applied in one system does not reach the copy in the other. For a CPA firm it means a return exists in two states during the one month you cannot afford ambiguity.
Permissions carried over from the acquired firm
Acquired environments almost always arrive with over-broad access. The departing owner’s account still has domain admin. A former contractor still has a mailbox. A shared folder is open to everyone because that was easier in a six-person office. None of it is malicious and all of it is now yours.
Nobody owns the seam
Each office has an idea of who handles IT. Neither idea covers the space between them. Tickets about cross-office issues sit because they are nobody’s obviously.
Compliance evidence fragments
If your firm is subject to Regulation S-P, you owe an incident response program covering customer information wherever it sits, including in the office you acquired last quarter. If you are a CPA firm, your Written Information Security Plan now has to describe an environment it was not written for. A WISP that describes one office while the firm operates three is not a WISP.
Opening a second office or closing on a merger? We run a pre-integration review that maps both environments and tells you what has to be resolved before close rather than after. Call (888) 352-4832 or request a review.
Our IT Can’t Keep Up With How Fast We’re Growing. What Are Our Options?
Three, and the right one depends on where the constraint actually sits.
Option
Fits when
Watch out for
Keep internal IT, add a co-managed partner
You have someone good who is simply outnumbered, and institutional knowledge matters
Needs a clear split of duties in writing, or both sides assume the other has it
Move to a fully managed provider
No internal IT, or the role has been a rotating side job
Documentation ownership on exit; settle it in the contract
Hire ahead of the growth
Rare. Works only if you can hire depth, not one generalist
One person cannot cover after-hours, security operations and compliance evidence
For most DFW professional firms between roughly 10 and 150 people, the co-managed route is the one that survives contact with a merger. It keeps the person who knows why the Plano office does things differently, and adds the capacity that a second office demands.
The Pre-Close Checklist
Run this before the deal closes, not after. Every item is cheaper to resolve while there is still negotiating leverage.
Inventory both environments. Every system holding client data, with an owner. See our IT due diligence definition for scope.
Get the acquired firm’s incident history. Ask directly whether they have had a breach, and what was disclosed. Inheriting an undisclosed incident is inheriting its notification obligation.
Check licensing transferability. Practice management and document management licences frequently do not survive a change of control without renegotiation.
Identify the data owner of record. For client files, who is the custodian after close, and does the engagement letter say so.
Confirm the acquired firm’s vendor list. Their service providers become your service providers, and under Reg S-P you owe oversight of them.
Set the identity cutover date before close. If it is not scheduled, it will not happen.
Frisco, Plano and Irving: Where the Consolidation Is Happening
Frisco sees the most greenfield second offices. Firms that started here are opening additional locations rather than acquiring them, which is the easier version of this problem: one culture, one set of standards, and a chance to do identity correctly from the start. DKBinnovative is headquartered in Frisco, and our Managed IT Frisco team handles a steady flow of these expansions. For firms in the finance vertical specifically, our Managed IT Frisco practice covers the compliance overlay.
Plano is where most of the genuine mergers happen, because it holds the region’s concentration of established firms with founders approaching succession. These are the hardest integrations: two mature environments, two sets of habits, twenty years of accumulated data on each side. Our Managed IT Plano engagements with professional firms frequently start the month after a close, and our Managed IT Plano security team handles the permissions cleanup that always follows.
Irving and Las Colinas tends to produce the satellite office rather than the merger. Firms headquartered elsewhere in the metroplex open a Las Colinas presence to sit closer to corporate clients, which means a small office with full compliance obligations and no local IT. Our Managed IT Irving practice works from an office at 7301 State Hwy 161, and our Managed IT Irving team covers exactly this pattern.
Frequently Asked Questions
What are the best managed IT services for multi-location businesses?
The best managed IT services for multi-location businesses centralize identity, data and policy while leaving each office’s local workflow alone: a single sign-on directory, one document repository with per-office permissions, uniform security baselines, and a support desk that knows which office a caller is in. Replicating one office’s setup onto the next produces parallel systems that drift.
How do you centralize IT for a growing multi-site company?
In this order: identity, then data, then policy, then applications, then network. Identity comes first because every compliance obligation depends on being able to say who had access to what and when, and two directories produce two answers. Firms that start with applications usually have to redo the work.
When should we integrate IT during a merger?
Assessment before close, execution after. The inventory, incident history, licensing check and vendor review all need to happen while you still have negotiating leverage. The cutover itself should be scheduled before close even if it runs afterwards.
Does our WISP or incident response plan need updating after we acquire a firm?
Yes. A Written Information Security Plan or Reg S-P incident response program describes a specific environment. Once the firm operates an additional office, a plan that describes only the original one no longer reflects reality, which is the first thing an examiner notices.
Can we keep our existing IT person through a merger?
Usually you should. A co-managed arrangement keeps the person who understands why each office works the way it does, while adding after-hours coverage, security operations and the integration capacity that one person cannot supply alongside daily support.
How long does multi-office IT integration take?
For a professional firm, expect 45 to 90 days from engagement to a stable consolidated environment, with identity work in the first few weeks. Complex integrations involving legacy on-premises systems on both sides run longer.
Working With DKBinnovative
We have supported professional firms across Dallas-Fort Worth since 2004, which is 22 years, and today covers 2,632+ end users across 55+ companies with a 78% first-call resolution rate and 98.14% client satisfaction. Our infrastructure standardizes on Microsoft Azure and Microsoft 365, and we deploy Hatz.AI where firms need governed AI that keeps client material inside their own tenant.
If you are looking at a second office or a merger, the most useful thing we can do is look at both environments before you close and tell you plainly what has to be resolved first.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-October3.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-19 12:05:192026-10-02 10:07:16Multi-Office IT for Law, CPA and RIA Firms in Frisco, Plano & Irving
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
IT support for law and accounting firms is a different discipline from general business IT, and firms in Frisco, Plano and Irving usually find that out the hard way.
A litigation boutique off Legacy Drive in Plano loses access to its document management system on the Thursday before a Monday filing deadline. A four-partner CPA practice in Frisco discovers in late February that a staff mailbox has been forwarding client returns to an outside address since December. A corporate firm in Las Colinas gets a client security questionnaire that asks, in writing, whether its IT vendor carries cyber liability coverage and who reviews its access logs.
None of these are hypothetical. They are the three ways professional firms in Dallas-Fort Worth discover that IT support for law and accounting firms is a different discipline from general business IT: a deadline, a breach, and a client asking a question the firm cannot answer.
This guide covers what law and accounting firms in Frisco, Plano and Irving need from an IT partner in 2026, which obligations are genuinely binding, and how to tell a specialist from a generalist with a legal page on their website.
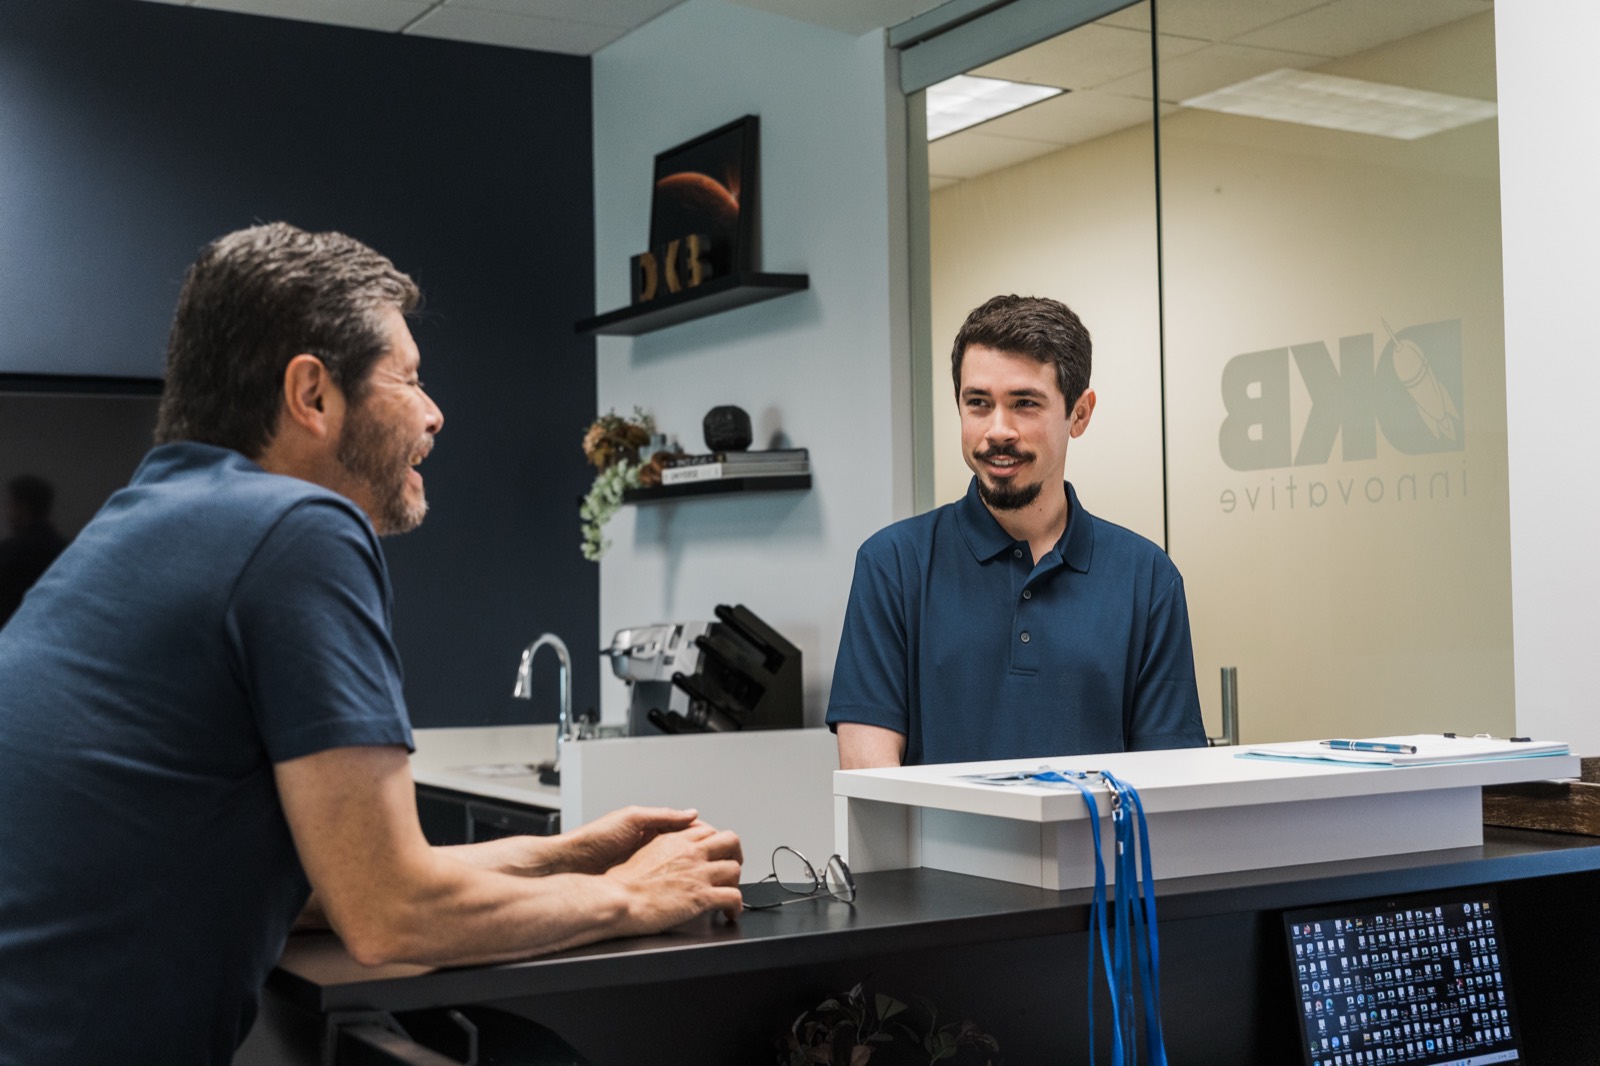
Client-facing from day one. Most firms meet us across a desk like this.
Who Specializes in IT Support for Law and Accounting Firms?
Firms that specialize in IT support for law and accounting practices build their service around three things a general MSP does not handle: professional-responsibility duties like the ABA’s confidentiality and breach-notification opinions, federal safeguards rules that treat accountants as financial institutions, and evidentiary requirements such as legal hold and defensible retention. The technical stack matters less than whether the provider can produce evidence when a regulator or a client asks.
That last sentence is the whole distinction. Most MSPs can deploy endpoint protection and patch a server. Far fewer can hand a managing partner a dated access review, a retention policy mapped to a records rule, and an incident response plan that names who calls the client and within how many days.
The seven capabilities below are what this desk is actually staffed to cover.
The Three Rulebooks That Actually Bind Your Firm
Professional firms are frequently sold compliance in the abstract. It is more useful to know precisely which rules apply to you, because they differ sharply between a law practice and an accounting practice.
For law firms: ethics opinions, not statutes
Lawyers are not regulated by a federal cybersecurity agency. They are bound by professional conduct rules, and three ABA formal opinions carry most of the weight:
Formal Opinion 477R (2017) addresses securing communication of protected client information, and makes clear that unencrypted email is not automatically sufficient when the sensitivity of the matter is high.
Formal Opinion 483 (2018) sets out what a lawyer owes clients after a breach. It defines the triggering event narrowly, as an episode where material client confidential information is misappropriated, destroyed or compromised, or where the lawyer’s ability to perform the work is significantly impaired. When that threshold is met, Model Rule 1.4 requires the firm to keep current clients reasonably informed.
Formal Opinion 498 (2021) covers virtual practice, which for most DFW firms now describes ordinary Tuesday operations rather than an exception.
Two supporting rules do quiet work underneath these. Model Rule 1.1 and its technology comment require lawyers to keep up with the benefits and risks of relevant technology. Model Rules 5.1 and 5.3 require supervision of others, and that explicitly reaches third-party electronic information storage vendors. Your IT provider is not outside your ethical perimeter. Supervising them is part of the duty.
For accounting firms: you are a financial institution
CPA firms and tax preparers are covered by the Gramm-Leach-Bliley Safeguards Rule. That surprises a lot of partners, but it is settled: preparing returns for compensation makes a practice a financial institution for these purposes.
The practical consequence is the Written Information Security Plan. Federal law requires tax and accounting professionals to create and maintain a WISP, and the IRS has published two documents that function as the working standard: Publication 4557, Safeguarding Taxpayer Data, and Publication 5708, which walks a practice through building the plan itself. The IRS and its Security Summit partners reissued that reminder in August 2026.
A WISP is not a document you buy once. It names a responsible individual, records a risk assessment, and gets reviewed and updated. If your current provider has never asked to see yours, that is a signal.
For firms serving investment clients: Reg S-P reaches your vendors
If your firm works with registered investment advisers, be aware that amended Regulation S-P took full effect for smaller entities on June 3, 2026, after applying to larger entities from December 3, 2025. It obliges covered institutions to oversee their service providers. Advisory clients are now passing that obligation down the chain in the form of questionnaires. We cover the detail in our companion piece on managed IT for RIA and wealth management firms.
Is a Specialized IT Partner Right for Your Firm?
Not every practice needs one. A solo practitioner running a cloud practice management suite on two laptops is usually fine with good habits and a consumer backup service.
The economics change at a predictable point. In our experience across 55+ client companies and 2,632+ supported end users, firms benefit from a specialized partner when they hit roughly these conditions:
Somewhere between 10 and 150 people, which is large enough that informal coordination fails and small enough that a full internal IT department is hard to justify
More than one office, or a genuine hybrid pattern where staff move between home and a Frisco or Las Colinas location
Client security questionnaires arriving at least a few times a year
An existing WISP or incident response plan that nobody has revisited in over a year
Any practice area where a deadline is court-imposed rather than self-imposed
Firms with an internal IT manager often get more value from a co-managed arrangement than from replacing that person. The internal manager keeps relationships and institutional knowledge; the partner supplies after-hours coverage, security tooling and the compliance evidence work.
Not sure which obligations apply to your practice? We run a no-cost review that maps your firm against the ABA opinions, the Safeguards Rule and your clients’ vendor requirements. Call (888) 352-4832 or request a review.
Seven Things a Legal or Accounting IT Provider Must Cover
Use this as a checklist when you evaluate anyone, including us.
1. Identity, not just antivirus
Most firm breaches now start with a credential, not malware. Phishing-resistant multifactor authentication on every account, conditional access that restricts sign-ins by location and device health, and privileged accounts held separately from daily-use accounts. On Microsoft 365, which is where the overwhelming majority of DFW professional firms live, this is configuration work rather than new spend.
2. Mailbox forwarding and delegation monitoring
The February CPA scenario at the top of this article is one of the most common incidents we see in tax season. Business email compromise usually announces itself through a quietly created forwarding rule. Alerting on rule creation, external forwarding and unusual delegate permissions catches it in hours instead of months.
3. Legal hold and defensible retention
For litigation practices this is not optional. You need the ability to preserve a custodian’s mail and files without the custodian being able to delete, and a record showing when the hold was applied. Retention settings that silently purge items after a fixed window will eventually collide with a preservation duty.
4. Encryption with a client-communication policy attached
Opinion 477R does not require encrypting everything. It requires judgment about sensitivity. That means your provider should help you build a usable rule, for example that matters involving personal financial data, health information or sealed filings go through a secure portal rather than attachments, and then make the secure path the easy one. Security controls that staff route around are not controls.
5. Backup that has actually been restored
Ask when your last restore test ran and what it produced. A backup job showing green is a claim; a completed restore is evidence. For firms with a filing calendar, we recommend documented recovery objectives per system, with the document management platform and time and billing treated as tier one.
6. Vendor and subcontractor oversight
Model Rules 5.1 and 5.3 put supervision of storage vendors on the firm. Reg S-P puts service provider oversight on your advisory clients, who then push it to you. Practically, this means keeping a current inventory of every system holding client data, with an owner and a review date against each entry.
7. Secure AI, governed before it spreads
Staff at professional firms are already using AI tools, with or without a policy. The risk for a law or accounting practice is not AI itself, it is client-confidential text leaving the firm’s control and entering a public model. We deploy Hatz.AI for this reason: it gives a firm a private, governed environment where matter content stays inside the tenant and administrators can see what was used. Getting a governed option in place early is far easier than clawing back shadow usage later.
What This Looks Like in Frisco, Plano and Irving
The three markets behave differently, and a provider who cannot describe the difference probably does not serve them.
Frisco has grown a dense population of newer, fast-scaling practices, many of them spun out of larger Dallas firms and built cloud-first from day one. The typical engagement here is less about migrating legacy servers and more about imposing governance on an environment that grew quickly without it. DKBinnovative is headquartered in Frisco, which means our Managed IT Frisco engagements get on-site response measured in minutes rather than hours. For firms wanting the broader service view, our Managed IT Frisco page covers the full scope.
Plano holds the region’s heaviest concentration of established mid-sized professional firms, including a lot of practices with 20 to 40 years of history and the accumulated systems that implies. Work here often starts with untangling an on-premises file server that three generations of IT vendors have touched. Our Managed IT Plano team handles a high share of these consolidations, and our Managed IT Plano security practice covers the financial-firm side specifically.
Irving and Las Colinas is the market most often overlooked, and in our view the most interesting for professional firms. The Las Colinas corridor carries a corporate tenant base that produces a steady stream of outside counsel and audit relationships, which means firms there face enterprise-grade vendor security reviews earlier in their growth than firms elsewhere in the metroplex. Our Managed IT Irving practice operates from an office at 7301 State Hwy 161 in Las Colinas, and our Managed IT Irving security work leans heavily toward questionnaire readiness for exactly this reason.
IT Outsourcing for Professional and Financial Services Firms
IT outsourcing for professional and financial services firms differs from general business outsourcing in one respect: the provider inherits part of your regulatory obligation. Because ABA Model Rules 5.1 and 5.3 require supervision of storage vendors, and Reg S-P requires oversight of service providers, an outsourcing arrangement in these sectors is a compliance relationship, not just a support contract.
That reframes how you scope the engagement. The contract needs to say who retains data, who notifies whom on an incident, how quickly, and what evidence the provider will produce when your client or regulator asks. Firms that outsource on price alone tend to discover these gaps during the one week they cannot afford to.
In-House IT vs. a Specialized MSP for Professional Firms
Capability
One internal IT person
Generalist MSP
Specialized professional-services MSP
After-hours and filing-deadline coverage
Limited to their availability
Usually tiered or extra
Included, with named escalation
ABA opinion and WISP familiarity
Varies widely
Rare
Core competency
Client security questionnaire support
Falls to a partner
Ad hoc
Standard deliverable
Legal hold and retention
Depends on the individual
Often unsupported
Configured and documented
Security tooling depth
Constrained by budget
Good
Good, plus evidence of operation
Continuity when someone leaves
Single point of failure
Covered
Covered, with documentation held jointly
The honest caveat: a strong internal IT manager who understands your practice is genuinely valuable, and replacing them with an outside vendor is usually a downgrade. The better pattern is to keep them and add the depth around them.
How to Evaluate a Provider in One Meeting
Five questions separate specialists from generalists quickly.
“Show me a client security questionnaire you completed in the last quarter.” Redacted is fine. If nothing exists, they have not been through the exercise.
“What is your documented process when a client mailbox is compromised during tax season?” Listen for containment sequencing and who notifies whom, not for product names.
“How would you apply a legal hold in our environment?” A specialist answers with a platform and a procedure. A generalist asks what a legal hold is.
“When did you last complete a restore test for a firm like ours, and what broke?” The second half is the real question. Everyone’s restores have surprises; only honest providers describe them.
“Who owns the documentation if we leave?” Firms that hold environment documentation hostage exist. Settle it before you sign.
Does a small law firm really need a specialized IT provider?
Below roughly ten people, usually not. The obligations still apply, but a disciplined solo or small practice can meet them with good cloud hygiene. The case for a specialist strengthens once you add staff who are not partners, because supervision duties under Model Rules 5.1 and 5.3 become harder to discharge informally.
Are accounting firms legally required to have a written security plan?
Yes. Tax and accounting professionals are required under federal law to create and maintain a Written Information Security Plan. IRS Publications 4557 and 5708 are the practical references, and the plan should be reviewed and updated rather than written once and filed.
What happens if our firm suffers a breach?
For law firms, ABA Formal Opinion 483 governs the duty to notify current clients, triggered when material confidential information is compromised or the firm’s ability to perform the work is significantly impaired. For accounting firms, the WISP obligations include reporting an incident affecting 500 or more individuals within 30 days. State breach notification law may apply on top of both.
Can we keep our internal IT person and still use a managed provider?
Yes, and for firms with existing internal IT this is usually the better arrangement. A co-managed model keeps your internal knowledge in place while adding after-hours coverage, security operations and the compliance documentation work that a single person cannot sustain.
How long does onboarding take?
For a professional firm, expect 45 to 90 days from signature to steady state. Discovery and documentation take the first few weeks, security baseline work follows, and compliance artifacts like the WISP review and access reviews come once the environment is stable.
Working With DKBinnovative
We have supported professional firms across Dallas-Fort Worth since 2004, which is 22 years of watching what actually goes wrong in practices like yours. Today that includes 2,632+ end users across 55+ companies, a 78% first-call resolution rate, and 98.14% client satisfaction. Our infrastructure work standardizes on Microsoft Azure and Microsoft 365, and our secure AI deployments run on Hatz.AI so that client-confidential material stays inside your tenant.
If your firm is in Frisco, Plano or Irving and you are weighing a change, the most useful next step is usually the smallest one: let us map your current environment against the obligations that actually apply to your practice area, and tell you plainly where the gaps are.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-October.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-18 11:39:332026-09-18 11:42:28IT Support for Law and Accounting Firms in Frisco, Plano & Irving
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
For two years, amended Regulation S-P was a deadline. Firms tracked it on a compliance calendar, assigned it to someone, and worked toward a date.
Both dates have now passed. Larger entities came into scope on December 3, 2025. Smaller entities, which includes SEC-registered investment advisers with less than $1.5 billion in assets under management, came into scope on June 3, 2026.
That changes the nature of the question. Reg S-P is no longer a project with a due date. It is a standing condition your firm is either meeting or not, and the way it now surfaces is through an examination request or a client’s vendor questionnaire. The operative word has shifted from “prepare” to “evidence.”
This piece covers what a firm in Frisco, Plano or Irving must be able to show today, and specifically which parts of it are IT problems rather than compliance-department problems.
Reg S-P is now an evidence problem, not a calendar one.
How Can IT Services Help Meet SEC Cybersecurity Guidance?
IT services meet SEC cybersecurity guidance by producing evidence, not just protection. Reg S-P requires a written incident response program, the ability to detect unauthorized access to customer information, customer notification within 30 days of becoming aware of an incident, and documented oversight of service providers. Each of those obligations depends on logging, alerting, retention and access records that only the technology environment can supply.
The distinction matters because firms routinely buy security tooling and still fail an examination. A firm can run good endpoint protection and still be unable to answer the question an examiner actually asks, which is some version of: show me how you would know, show me when you knew, and show me what you did.
Detection is a rule requirement. Someone has to be watching.
What the Amended Rule Actually Requires
The amendments adopted May 16, 2024 updated a rule that had been largely unchanged since 2000. Four elements carry the operational weight.
1. A written incident response program
Covered institutions must maintain written policies and procedures for an incident response program reasonably designed to detect, respond to and recover from unauthorized access to or use of customer information. All three verbs matter. Detection is the one most firms underinvest in, because it is the least visible until it is needed.
2. The 30-day notification clock
When sensitive customer information was, or is reasonably likely to have been, accessed or used without authorization, the firm must notify affected individuals as soon as practicable and no later than 30 days after becoming aware that the incident occurred or is reasonably likely to have occurred.
Read that trigger carefully. The clock starts at awareness of a reasonably likely incident, not at confirmation of a confirmed breach. Firms that wait for certainty before starting the count are misreading the standard. The notice itself must describe the incident, the information involved, and what affected individuals can do to protect themselves.
3. Broader scope of covered information
The safeguarding and disposal requirements now apply to all customer information, defined as any record containing nonpublic personal information about a customer of a financial institution that is in the firm’s possession, or that is handled or maintained by the firm or on its behalf.
The phrase “or on its behalf” is the one that expands the perimeter. Data sitting with your custodian, your CRM vendor, your portfolio accounting platform or your outsourced IT provider is inside your obligation.
4. Service provider oversight
Firms must take reasonable steps to require service providers to protect customer information and to notify the firm of a breach. In practice this has produced a wave of questionnaires flowing downstream, which is why professional firms serving advisory clients are now fielding security reviews they never used to see.
One additional change is easy to miss: transfer agents registered with the Commission or another appropriate regulatory agency must now comply with both the safeguarding and the disposal requirements, where previously they faced only the disposal rules and only in some cases.
Who Counts as a “Smaller Entity”
The distinction only ever governed the compliance date, and both dates are now behind us. It remains useful for understanding where your peers are in their maturity curve.
Entity type
Larger entity threshold (complied by Dec 3, 2025)
SEC-registered investment adviser
$1.5 billion or more in assets under management
Investment company
Net assets of $1 billion or more at the most recent fiscal year end
Broker-dealer
Any that is not a small entity under the Exchange Act
Transfer agent
Any that is not a small entity under the Exchange Act
Most independent RIAs across Dallas-Fort Worth fell into the smaller-entity group and reached their date in June 2026. If your firm treated that as a documentation exercise and has not revisited it since, the gap between the written plan and the operating environment is probably where your risk now sits.
Can your firm evidence all four requirements today? We run a Reg S-P readiness review that tests the written plan against what your environment can actually produce. Call (888) 352-4832 or request a review.
The Six Gaps We Find Most Often
These come from readiness work with advisory firms across the metroplex. They are ordered by how frequently they appear, not by severity.
1. The plan names a role that no longer exists
Incident response plans written in 2024 and 2025 routinely name an individual who has since left, or a vendor the firm no longer uses. An examiner reading a plan that names a departed employee learns something about the firm beyond that one error.
2. Logs that do not reach back 30 days in a usable form
If you become aware of a possible incident on day one and need to determine scope, you need history. Default retention on many platforms is shorter than firms assume, and the retention that exists is often not searchable by the people who would need to search it at 9pm on a Friday.
3. No alerting on the events that signal unauthorized access
Detection is a rule requirement, not a best practice. At minimum a firm should alert on impossible-travel sign-ins, new mailbox forwarding rules, mass file downloads from document storage, and changes to privileged group membership. Each of these is a common first observable in an actual compromise.
4. A vendor inventory that is out of date or does not exist
Service provider oversight requires knowing who your service providers are. Firms often have an inventory built during the original compliance push and never maintained. Every system that touches customer information needs an entry, an owner and a review date.
5. Notification mechanics never tested
The 30-day clock assumes you can identify affected individuals and reach them. Many firms have never tested whether they can produce an accurate affected-party list from their systems under time pressure. That is a tabletop exercise, and it takes an afternoon.
6. Secure AI with no governance
Staff at advisory firms are pasting client information into public AI tools. This is now one of the more direct routes to an unauthorized-use problem, and it is invisible without a governed alternative. We deploy Hatz.AI so advisory firms get a private environment where client data stays inside the tenant and administrators retain visibility. Our deeper treatment is in secure AI for investment firms.
What to Look for in a Managed IT Provider Experienced With SEC Reg S-P Compliance
A provider experienced with Reg S-P should be able to do four specific things, and you can test each in a first conversation.
Map each rule requirement to a control and an artifact. Not “we do security,” but: detection maps to these alert rules, and the artifact is this report. If they cannot draw that line, they have not done this work.
Produce a completed vendor security questionnaire on request. Advisory clients push oversight downstream. Your IT provider is one of your service providers, and should already be answering for itself.
Run a notification tabletop. Ask them to walk through hour one through day thirty of a suspected incident at your firm, naming who decides what.
Retain evidence on a defined schedule. Ask what they keep, for how long, and how you get it if you leave.
Frisco, Plano and Irving: Three Different Advisory Markets
Frisco has attracted a concentration of newer independent RIAs, many founded by advisers who broke away from wirehouses in the last decade. These firms are typically cloud-native and technically current, but they crossed into Reg S-P scope while still operating with startup-era informality about documentation. Our Managed IT Frisco work with these firms is usually less about new tooling and more about turning existing capability into evidence. DKBinnovative is headquartered in Frisco, and our broader Managed IT Frisco practice supports firms across the corridor.
Plano holds many of the region’s established advisory practices and multi-family offices, firms with longer histories, more legacy systems and more accumulated data. Scope questions are harder here, because customer information has had 20 years to spread into file shares and archives nobody has catalogued. Our Managed IT Plano engagements with advisory firms often begin with discovery of where customer information actually lives, and our Managed IT Plano security team handles the remediation that follows.
Irving and Las Colinas carries a different profile again. The corridor’s institutional and corporate presence means advisory firms there interact with counterparties who run serious vendor due diligence, so the questionnaire pressure arrives earlier and lands harder. Our Managed IT Irving practice works from an office at 7301 State Hwy 161 in Las Colinas, and our Managed IT Irving team spends a disproportionate share of its time on evidence packages for exactly these reviews.
Frequently Asked Questions
Has the Reg S-P compliance deadline passed?
Yes, both of them. Larger entities had to comply from December 3, 2025, and smaller entities from June 3, 2026. There is no remaining runway. A firm that is not currently meeting the requirements is out of compliance rather than behind schedule.
What is a managed IT provider experienced with SEC Reg S-P compliance responsible for?
The provider is responsible for the technical capability behind each requirement: detection and alerting on unauthorized access, log retention sufficient to determine scope, the access and configuration records that evidence safeguarding, and its own conduct as one of your service providers. The firm retains responsibility for the written program, the notification decision and the regulatory relationship.
Does Reg S-P apply to our firm if we are a small RIA?
If you are registered with the SEC, yes. Assets under management determined only which compliance date applied to you, not whether the rule reaches you. Firms under $1.5 billion in AUM were in the smaller-entity group with a June 3, 2026 date.
When does the 30-day notification clock start?
It starts when the firm becomes aware that an incident involving unauthorized access to sensitive customer information has occurred, or is reasonably likely to have occurred. That is an awareness-of-likelihood standard, not a confirmation standard, so the clock can start before an investigation concludes.
Do we have to oversee our IT provider under Reg S-P?
Yes. Covered institutions must take reasonable steps to require service providers to protect customer information and to notify the firm of a breach. An IT provider that cannot complete your security questionnaire creates a compliance problem for you, not only an inconvenience.
How long does a Reg S-P readiness engagement take?
A readiness review takes a few weeks. If it surfaces material gaps, remediation and full onboarding typically run 45 to 90 days depending on how much discovery the environment requires.
Working With DKBinnovative
We have supported investment and professional firms across Dallas-Fort Worth since 2004. That is 22 years, currently spanning 2,632+ end users across 55+ companies, with a 78% first-call resolution rate and 98.14% client satisfaction. We standardize on Microsoft Azure and Microsoft 365 for infrastructure, and deploy Hatz.AI where firms need governed AI that keeps client information inside their own tenant.
If your firm reached its Reg S-P date and has not revisited the program since, the useful next step is a short readiness review that tests the written plan against what your systems can actually produce. We will tell you plainly which of the four requirements you can evidence today and which you cannot.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-October2.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-17 11:57:342026-09-18 12:07:44Reg S-P Is Now in Force: What DFW Investment Firms Must Prove in 2026
Reviewed by Peter Bertran, Chief Client Officer, DKBinnovative
Post-quantum readiness is usually filed under problems for later. For a law firm it is not, because attorney-client privilege has no expiry date and encrypted traffic can be copied today and opened in a decade.
Most technology risks have a shape professional firms recognize. Something happens, you respond, you notify, you recover. This one is different. The damage would be done years before anyone knows, and the decision that determines whether it happens to you is being made now, quietly, by whoever controls how your firm encrypts data in transit.
This is not a prediction about when a cryptographically relevant quantum computer arrives. Nobody credible will give you that date. It is about a much narrower question: how long does your firm’s confidential material need to stay confidential, and is that longer than the time remaining before today’s encryption stops holding?
For a great many law, CPA and investment firms in Dallas-Fort Worth, the honest answer is yes.
Readiness starts with knowing what protects what.
What Is Harvest Now, Decrypt Later?
Harvest now, decrypt later is an attack in which encrypted data is captured today and stored until quantum computing makes it decryptable. The attacker gains nothing at the moment of capture, so there is no breach to detect and nothing to notify. The exposure is realized years afterwards, which makes the risk a function of how long your data must stay secret rather than of how strong your encryption is today.
That reframing is the entire point. A firm asking “is our encryption strong enough?” is asking the wrong question. The right one is “how long does this need to hold, and will it?”
Early, not urgent. The distinction matters for budgeting.
Why This Lands Differently on Professional Firms
General business data has a short secrecy half-life. A price list stolen today and decrypted in 2034 is worthless. Professional firms hold the opposite kind of material.
Law firms: privilege does not expire
Attorney-client privilege survives the matter, the relationship and in most circumstances the client’s death. A privileged communication intercepted in encrypted form this year and opened in 2033 is still privileged, and its disclosure is still a harm. ABA Formal Opinion 477R already requires lawyers to make judgments about securing client communications based on sensitivity, and Model Rule 1.1’s technology comment requires keeping current with the risks of relevant technology. Neither of those obligations has a carve-out for risks that mature slowly.
Investment firms: retention outlasts the encryption
SEC recordkeeping obligations keep advisory records for years, and the customer information covered by Regulation S-P does not become harmless with age. Account numbers, tax identifiers and financial histories retain their value to an attacker far longer than a normal breach window. We cover the current obligations in our piece on what Reg S-P now requires firms to evidence.
CPA firms: the data is permanent by nature
A Social Security number does not get reissued because it was disclosed late. Tax records, beneficial ownership details and multi-year financial histories are among the longest-lived sensitive data any small firm holds, and the WISP obligations under IRS Publication 4557 apply to protecting it for as long as you hold it.
When Do Firms Need to Be Post-Quantum Ready?
Firms need to be post-quantum ready before the sum of their data’s required secrecy lifetime and their migration time exceeds the time remaining until quantum decryption is feasible. NIST has published the schedule that anchors this: quantum-vulnerable algorithms are deprecated after 2030 and disallowed after 2035, and the NSA’s CNSA 2.0 requires national security systems to migrate by 2030. A firm holding data that must stay confidential for ten years is already inside the window.
That arithmetic is worth doing explicitly, because it produces a different answer for different firms.
Firm type
Typical secrecy lifetime
Inside the window?
Litigation or corporate law firm
Indefinite; privilege does not lapse
Yes, clearly
RIA or wealth manager
Client lifetime plus estate administration
Yes
CPA or tax practice
Decades; identifiers never change
Yes
General commercial business
Months to a few years
Usually not yet
This is why the generic advice aimed at small business, which amounts to wait and see, is wrong for professional firms specifically. The waiting is the exposure.
Want to know where your firm’s long-lived data actually sits? We run a cryptographic inventory as part of our security assessment for professional firms. Call (888) 352-4832 or request one.
What Is Crypto-Agility, and Why Is It the Actual Deliverable?
Crypto-agility is the ability to change the cryptographic algorithms a system uses without rebuilding the system. It matters more than any individual algorithm choice, because the practical failure mode is not picking the wrong cipher. It is having encryption hard-coded into applications, appliances and integrations so deeply that changing it requires a project nobody has budgeted.
NIST published the first three post-quantum standards in 2024, including ML-KEM for key establishment and ML-DSA for digital signatures. Most firms will never touch those names. What they will experience is whether their vendors can turn the new algorithms on, and whether anyone at the firm knows which systems are waiting on which vendor.
What a Firm Should Actually Do This Year
None of this requires buying quantum anything. The useful work in 2026 is inventory and leverage.
Build a cryptographic inventory. Which systems hold or transmit data with a long secrecy lifetime, what protects it, and who supplies that protection. Most firms have never written this down, and it is the prerequisite for every later decision.
Classify by secrecy lifetime, not by sensitivity. These are different axes. A document can be moderately sensitive and need to stay secret for thirty years. That is the one that matters here.
Put the question to your vendors now. Ask your document management, practice management, portfolio accounting, email and VPN providers for their post-quantum roadmap in writing. You are not expecting a migration date. You are establishing that you asked, and finding out which vendors have no answer at all.
Prioritize data in transit. Harvest now, decrypt later is primarily an interception problem. Traffic crossing untrusted networks is the first thing to care about, ahead of data sitting on an encrypted disk in your office.
Fold it into what you already do. Add a post-quantum roadmap question to your vendor review cycle, and add long-lived data to your client security questionnaire evidence pack. This should cost you a meeting, not a project.
Write down the decision. Whatever you conclude, record that the firm considered it and why it chose the timeline it chose. For lawyers this is the technology-competence duty discharged in the only way that is provable later.
Three failure modes are already visible in how this topic gets sold.
Buying a product to solve it. There is no post-quantum appliance that makes a firm ready. Readiness is an inventory and a vendor posture, and anyone selling otherwise is ahead of the evidence.
Treating it as urgent. It is not urgent. It is early, which is a different thing and calls for a different budget. A firm that panics now will overspend on the wrong layer.
Ignoring it because the date is uncertain. The uncertainty cuts the other way. Because nobody can tell you when, a firm holding thirty-year secrets cannot argue it had time.
Frisco, Plano and Irving
Plano firms tend to hold the deepest archives, because the region’s established practices have twenty to forty years of accumulated matter files and client records. Long-lived data is exactly the exposure this creates, and it is usually spread across systems nobody has catalogued. Our Managed IT Plano team handles these inventories, and our Managed IT Plano security practice covers the financial-firm side.
Irving and Las Colinas firms will meet this first through someone else’s questionnaire. The corridor’s corporate and institutional clients run mature vendor diligence, and post-quantum roadmap questions have started appearing in enterprise assessments. Our Managed IT Irving practice works from an office at 7301 State Hwy 161, and our Managed IT Irving team tracks what is showing up in those reviews.
Frisco firms have the easiest version of this problem and the shortest path through it. Cloud-native practices inherit their cryptography from a small number of major platforms, which means readiness is largely a matter of knowing which platforms and keeping current. DKBinnovative is headquartered in Frisco; our Managed IT Frisco and Managed IT Frisco teams cover this work.
Frequently Asked Questions
What is harvest now, decrypt later?
Harvest now, decrypt later is an attack in which encrypted data is captured today and stored until quantum computing makes it decryptable. There is no breach to detect at the time of capture, so the risk is a function of how long your data must stay secret rather than of how strong your encryption is today.
When do firms need to be post-quantum ready?
Before the sum of their data’s required secrecy lifetime and their migration time exceeds the time remaining until quantum decryption is feasible. NIST deprecates quantum-vulnerable algorithms after 2030 and disallows them after 2035, and NSA CNSA 2.0 requires national security systems to migrate by 2030. A firm holding data that must stay confidential for ten years is already inside the window.
What is crypto-agility?
Crypto-agility is the ability to change the cryptographic algorithms a system uses without rebuilding the system. It matters more than any individual algorithm choice, because the common failure is encryption hard-coded into applications and appliances so deeply that changing it becomes an unbudgeted project.
Is this urgent for a small law or accounting firm?
It is early rather than urgent, and the distinction matters for budgeting. But it applies earlier to professional firms than to general businesses, because privilege does not expire and tax identifiers are never reissued. The work due this year is inventory and vendor questions, not spending.
Do we need to buy anything to become post-quantum ready?
No. There is no product that confers readiness. What a firm needs is a cryptographic inventory, a classification of data by secrecy lifetime, and written post-quantum roadmaps from the vendors that supply its encryption.
Does this affect our compliance obligations today?
Not directly. No current rule requires post-quantum migration for private firms. Indirectly it reaches lawyers through the technology-competence duty and reaches every firm through client security questionnaires, where post-quantum roadmap questions have begun to appear in enterprise vendor assessments.
Working With DKBinnovative
We have supported professional firms across Dallas-Fort Worth since 2004, which is 22 years, currently covering 2,632+ end users across 55+ companies with a 78% first-call resolution rate and 98.14% client satisfaction. Our infrastructure standardizes on Microsoft Azure and Microsoft 365, both of which are moving on post-quantum work at platform level, which is a large part of why cloud-native firms have a shorter path here.
If you want to know where your firm’s long-lived data sits and which vendors have an answer, that is a cryptographic inventory and it takes us a few weeks. It is the only part of this that is worth doing right now.
https://dkbinnovative.com/wp-content/uploads/2026/09/DKB-Covers_-October5.png54009600CS Dept.https://dkbinnovative.com/wp-content/uploads/2025/09/DKBinnovative-Blue-Logo-300x181.pngCS Dept.2026-09-15 12:09:192026-09-18 12:09:35Post-Quantum Readiness for Law, CPA and Investment Firms in DFW